Endpoint Protection gives you better control over your machines and their secrets
 Release Date: November 18, 2026
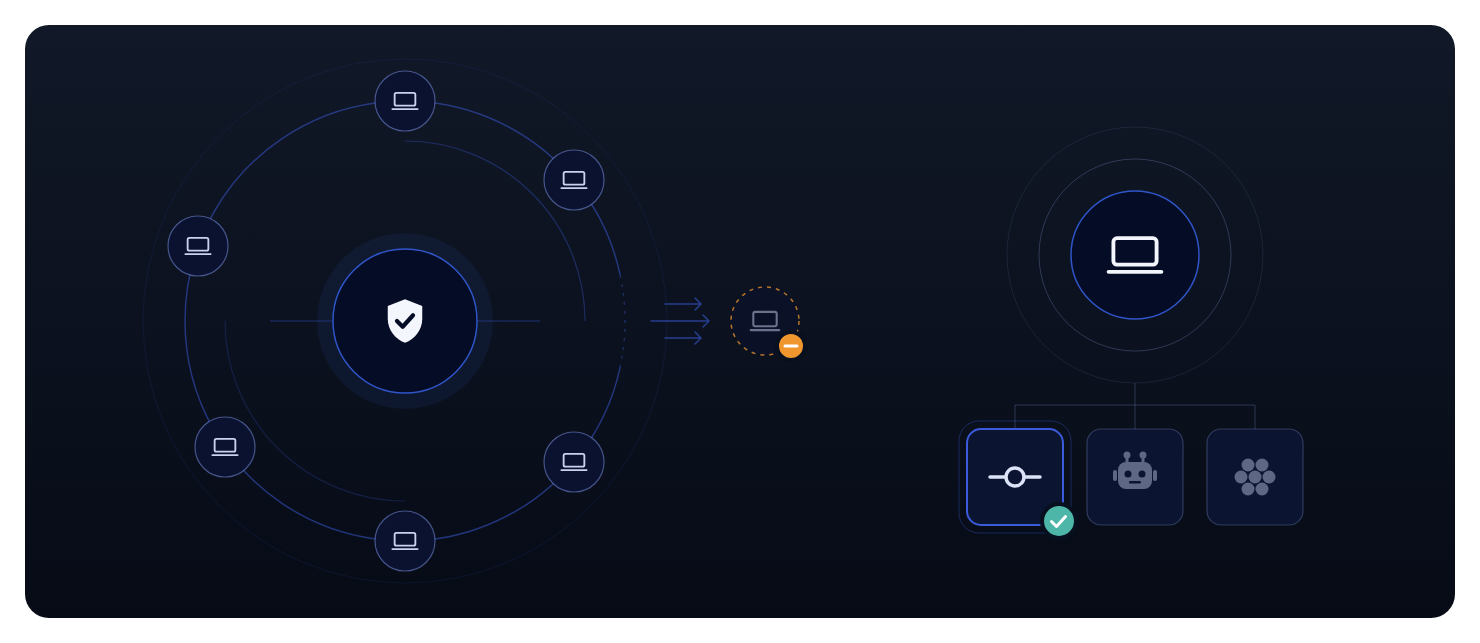
Endpoint Protection now shows which developer machines stop secrets before they are committed. Machine Scan checks each git repository on a machine for the ggshield pre-commit hook. The Endpoints dashboard shows the result next to AI hooks and honeytokens, in one Protection view. Admins can also remove machines that left the company. Pre-commit protection ships in the Machine Scan plugin 0.67 for ggshield.
What does this mean for you?
- Know which machines check commits: a new Pre-commit protection card shows the share of endpoints with the hook installed. One click filters the table to the endpoints without it.
- All protections in one column: a Protection column replaces the Honeytoken protection and AI agents columns. For each machine, it marks pre-commit, AI hooks and honeytoken as installed, missing, not applicable or compromised. Click it to see what is missing and how to fix it.
- One summary per machine: the endpoint detail page opens on a summary of the machine, its owner, OS and scanner version. It has one cell each for local scan, pre-commit, AI hooks and honeytoken.
- Remove retired machines: workspace admins can remove one or several endpoints from the Endpoints table. Removed endpoints leave the table, the coverage KPIs and the secrets list. A removed machine that sends a new scan comes back automatically.
- Read your fleet from the API:
GET /v1/endpoints/machineslists your machines and their users, so offboarding and incident response can start from a person or a machine. It needs the newendpoints:readscope, available to managers and above.
Why is this important?
The pre-commit hook stops a secret before it reaches a repository, a CI log or a fork. Until now, you could not see which machines ran it. Removing retired machines keeps your coverage numbers accurate.
Get Started Today!
Endpoint Protection is available for workspaces with a Growth or Enterprise plan. Talk to your Customer Success Manager to enable it, or contact us to upgrade your plan.
Update the plugin on each machine with ggshield plugin install machine_scan, or let your MDM job do it on its next run. Pre-commit protection shows after the next scan with plugin 0.67 or later. See Deploy ggshield at scale.
To install the pre-commit hook on the machines without it, add ggshield machine setup to your MDM job. This command also configures AI hooks and plants a honeytoken. See Setup and doctor options.
Enhancements
- Machine Scan:
- See pre-commit protection for each repository on the Repositories page of the local dashboard (
ggshield machine dashboard). - Add folders to every scan with the new
scan.extra_rootssetting inmachine_scan.yaml. - Point
REQUESTS_CA_BUNDLEto a folder of CA certificates, which Machine Scan trusts in addition to the operating system certificates. - Redact secrets in IPython history databases, and redact directly from the History & logs view of the local dashboard.
- On Linux, Machine Scan now skips sshfs 3.x and rclone mounts as remote drives.
- See pre-commit protection for each repository on the Repositories page of the local dashboard (
Fixes
- Machine Scan:
- Fixed an issue where Machine Scan skipped a private repository because one of its remotes was public.
- Fixed an issue where the local report database grew to several gigabytes on some machines.
- Fixed an issue where a scan ran out of memory on some dense files.
- Fixed an issue where
ggshield machine scanandggshield machine reportrejected--include-root. - Fixed an issue where
ggshield machine report --instanceread its settings from the default instance. - Fixed an issue where redacting one secret in the local dashboard also hid the secrets next to it.
- Fixed an issue where Machine Scan did not check Kubernetes service account tokens against their cluster.

