2 posts tagged with "endpoint-protection"

View All Tags

See all your AI agents across the fleet. Stop them leaking your secrets.

calendar icon   Release Date: September 7, 2026

AI discovery: agents, MCP servers, and AI Hooks across the fleet

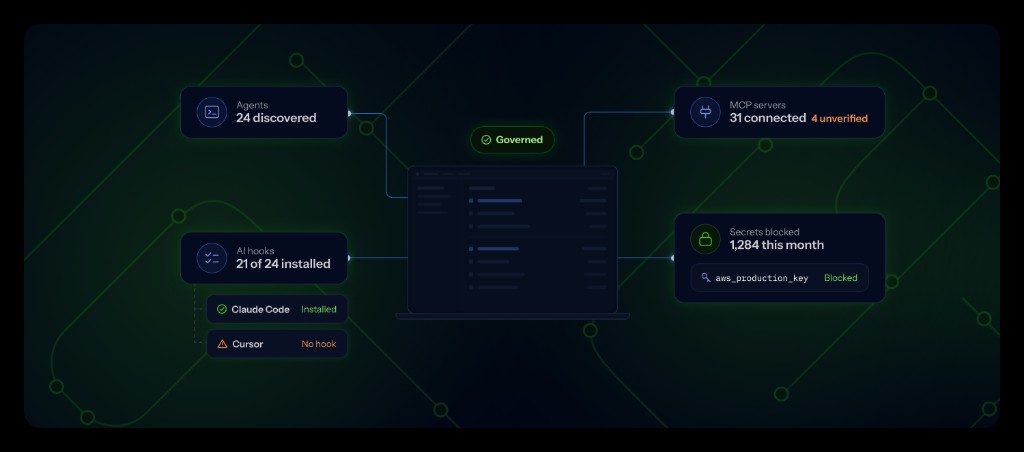
AI agents read files, run commands, and call MCP servers on your developers' behalf. Most teams cannot say which agents are deployed across the fleet, and which of them touch credentials. Secrets that leave in a prompt or tool call never hit a commit or a pull request, so your existing controls never see them.

Developer Endpoint Protection now does both:

What does this mean for you?

  • Codex and Mistral Vibe: AI Hooks now cover them alongside Claude Code, Cursor, Copilot CLI, and VS Code. They scan prompt submission, pre-tool use, and post-tool use. A block names the secret and how to remove it, so the developer or agent can fix and retry.
  • One command per machine: ggshield machine setup configures the hooks for every detected AI agents on the machine, along with git hooks.
  • Shadow AI you can see: the inventory reports agents and MCP servers per endpoint, hook coverage, and whether an agent's subscription is personal or company.
  • Faster incident response: after a compromise, you know which agents were on the machine, which MCP servers they used, and what those servers could reach. Add --history to ggshield ai discover to get the MCP tool calls parsed from the agent's transcripts.

Why is this important?

Developers using AI coding tools leak secrets at roughly twice the baseline rate. GitGuardian found 24,008 unique secrets in public MCP configuration files in 2025 cf. The State of Secrets Sprawl 2026.

Hooks stop the leak at the tool. The inventory tells you where to look.

Get started now

  1. Upgrade ggshield to 1.54.0 or later.
  2. Follow the Developer Endpoint Protection deployment docs to roll it out across the fleet.

Enhancements

  • Team Perimeter: Added a workspace setting to automatically remove sources deleted on the remote from team perimeters, while keeping them accessible to workspace managers.
  • NHI Governance: AWS access keys stored in a secrets manager, Vault, or Kubernetes are now linked to their AWS IAM identity in the identity map.

Fixes

  • Incidents: Fixed an issue where source locations were recomputed too frequently, causing excessive repository clones and bandwidth usage.
Catch credential stealers on your endpoint fleet

calendar icon   Release Date: August 10, 2026

Honeytokens on endpoints

Credential stealers do not hunt around a developer machine, they go straight for the handful of files where developers keep their secrets.

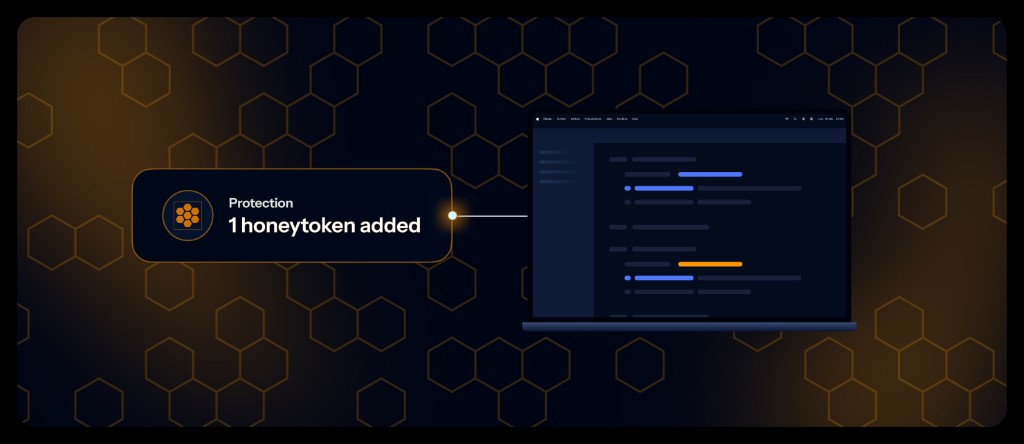
Endpoint Protection already gives you a full inventory of the credentials sitting in those files, and it now adds intrusion detection to that same deployment: ggshield plants a decoy AWS credential exactly where the stealers look first. The decoy opens nothing, so nobody has a reason to touch it. The moment someone does, you get an alert that names the compromised endpoint.

What does this mean for you?

  • A tripwire on the surface attackers hit first: stealers arrive through malicious packages, trojanized tools, and rogue browser extensions. Whichever way they get in, reading that credential file is their first move, and that move is now what exposes them.
  • Alerts with no ambiguity: the decoy has no legitimate use, so any use of it is unauthorized by definition. There is no baseline to learn, no tuning, and no signature list to maintain.
  • A last line of defense: if malware has already slipped past your EDR and other endpoint controls, using the decoy still gives it away.
  • A named machine to investigate: each event carries the IP address, user agent, and timestamp, and resolves to a specific endpoint and its owner.
  • Coverage you can measure: a new Honeytoken protection card in the Endpoints dashboard reports the share of your fleet that is protected and lists the endpoints that are not, so you can drive coverage to completion.
  • No new agent to deploy: planting reuses the ggshield binary you already install for scanning and writes a file rather than running a resident process.

Why is this important?

Credentials on developer machines have been a blind spot for a long time. Repository scanning, CI checks, and collaboration tool monitoring only ever see secrets that leave the laptop, while the credentials that stay local are exactly the ones harvesting malware is built to collect. Endpoint Protection brought those credentials into your inventory. It now watches for the theft itself, at the moment it happens, on a surface where most organizations have no detection at all.

For developers, this is invisible. Planting only ever touches its own credential profile and leaves every other profile on the machine untouched.

Start securing your endpoint fleet now!

Honeytoken protection is available now for workspaces with Endpoint Protection on a Business or Enterprise plan. If you already run endpoint scanning, adding it means nothing more than one MDM job to update and one more scope on your service account token.

Enhancements

  • Public API: Added the ability to create Personal Access Tokens (PATs) and Service Account Tokens (SATs) programmatically via the API, enabling automated token rotation workflows. Tokens created via the API must have a finite TTL.
  • ggshield: Launched an Azure DevOps extension that lets admins add a ggshield secret scan job to every pipeline in their organization with a single pipeline decorator. See Azure Pipelines for details.
  • Perimeter management: Automatic monitoring and automatic scan toggles are now available on Jira Cloud, Jira Data Center, Confluence Cloud, Confluence Data Center, and Microsoft Teams. New spaces, projects, and channels discovered on these sources can be picked up and scanned without adding them by hand, the same way the VCS integrations already work.

Fixes

  • Audit Logs: Scans triggered via a Personal Access Token now emit an audit log event.
  • Incidents: Fixed a display error in the decoded claims panel of a JWT secret. Malformed timestamp or scope claims, and payloads that are not a JSON object, now fall back to the raw value instead of breaking the panel.
  • Issue Tracking Integration: Fixed the "Edit issue" dialog closing unexpectedly.
  • Notifications: Fixed an issue where the team name was not populated for notifiers when the workspace contained more than 100 teams.
  • Access Management: Fixed an issue where deactivated members were incorrectly displayed in the grant access dialog.
  • GitHub Checkruns integration: Fixed an issue where a disabled detector could still block pull requests.
  • JFrog Artifactory Integration: Fixed an issue where the JFrog Container Registry reachability check did not route through ggbridge.
  • GitLab Integration: Fixed an issue where GitLab sources appeared as monitored in the integration settings but were not reflected in the perimeter view.