Integrate Azure Container Registry
Secure your containerized applications by monitoring Azure Container Registry for exposed secrets in container images and Docker configurations.
Why Monitor Azure Container Registry?
Azure Container Registry hosts the container images that power your Azure applications and services. These images frequently contain Azure service principal credentials, storage account keys, and database connection strings that provide direct access to your Azure infrastructure, making any secret exposure a critical threat to your entire cloud environment.
Capabilities
| Feature | Support | Details |
|---|---|---|
| Historical Scanning | ✅ (Supported) | Analyze existing images and their layers |
| Incremental Scanning | ✅ (Supported) | Regular scheduled scanning for new content |
| Monitored Perimeter | ✅ (Supported) | Granular monitoring of your repos |
| Team Perimeter | ✅ (Supported) | Team-based access control |
| Presence Check | ❌ (Not Supported) | All occurrences considered present |
| Source Visibility | ❌ (Not Supported) | All sources are considered as private |
| File Attachments | N/A | Not applicable for container registries |
What we scan:
- All container image layers
- Dockerfiles and build configurations
- Environment variables in image metadata
This integration automatically scans your monitored repositories, downloading Docker images which may incur bandwidth costs. To optimize costs and reduce false positives, carefully select the sources to monitor and use our filepath exclusion feature.
Plan requirements: Available for GitGuardian Enterprise plan. Try it for free with a 30-day trial - any detected incidents remain accessible after the trial ends.
Detector coverage: To minimize false positives, Generic High Entropy Secret and Generic Password are disabled. All other detectors are enabled.
Setup your Azure Container Registry integration
Prerequisites:
- Owner or Manager account on your GitGuardian Dashboard
- Azure admin permissions to create tokens in your Azure Container Registry
- Network connectivity between GitGuardian and your self-hosted services. Check out GitGuardian Bridge to enable secure connections between GitGuardian SaaS and your self-hosted services in private networks.
GitGuardian integrates with Azure Container Registry via a Token with read-only access to your repositories.
You can install GitGuardian on multiple Azure Container Registry instances to monitor your repositories.
-
Make sure you're logged as an administrator in your Azure Portal
-
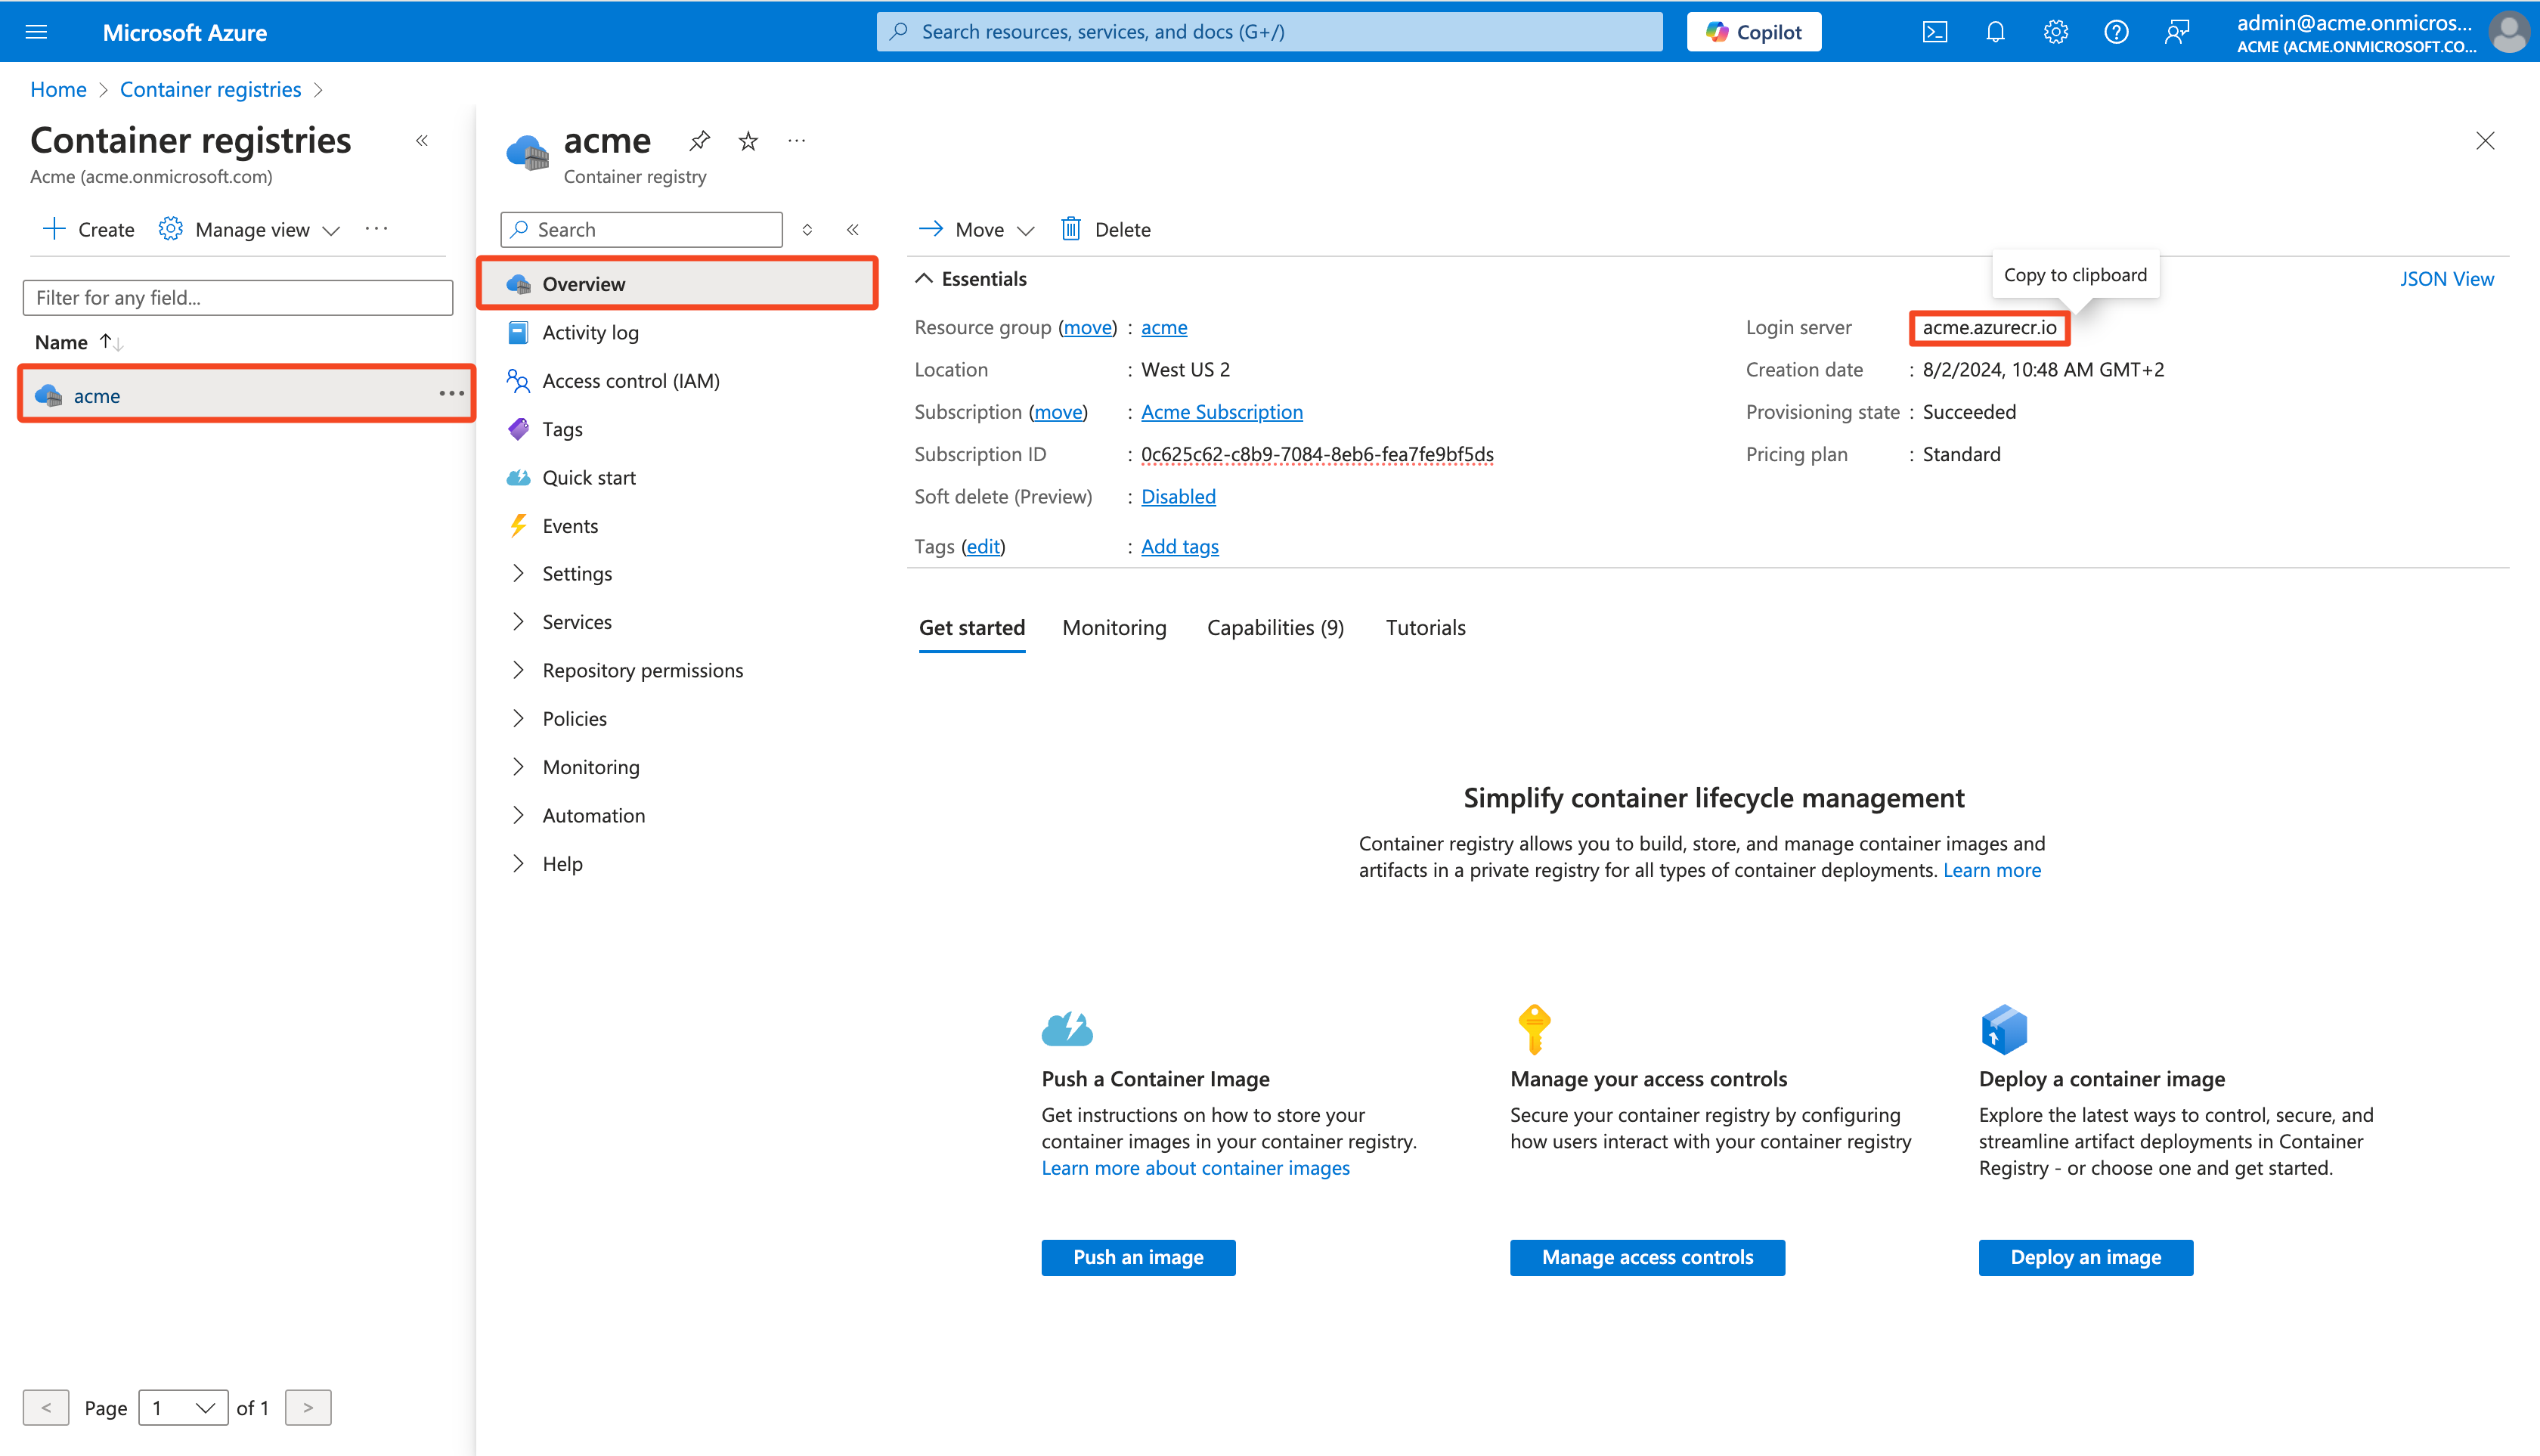
Browse your Container Registries and select the one you want to integrate
-
Go to the Overview section
-
Copy the Login server
-
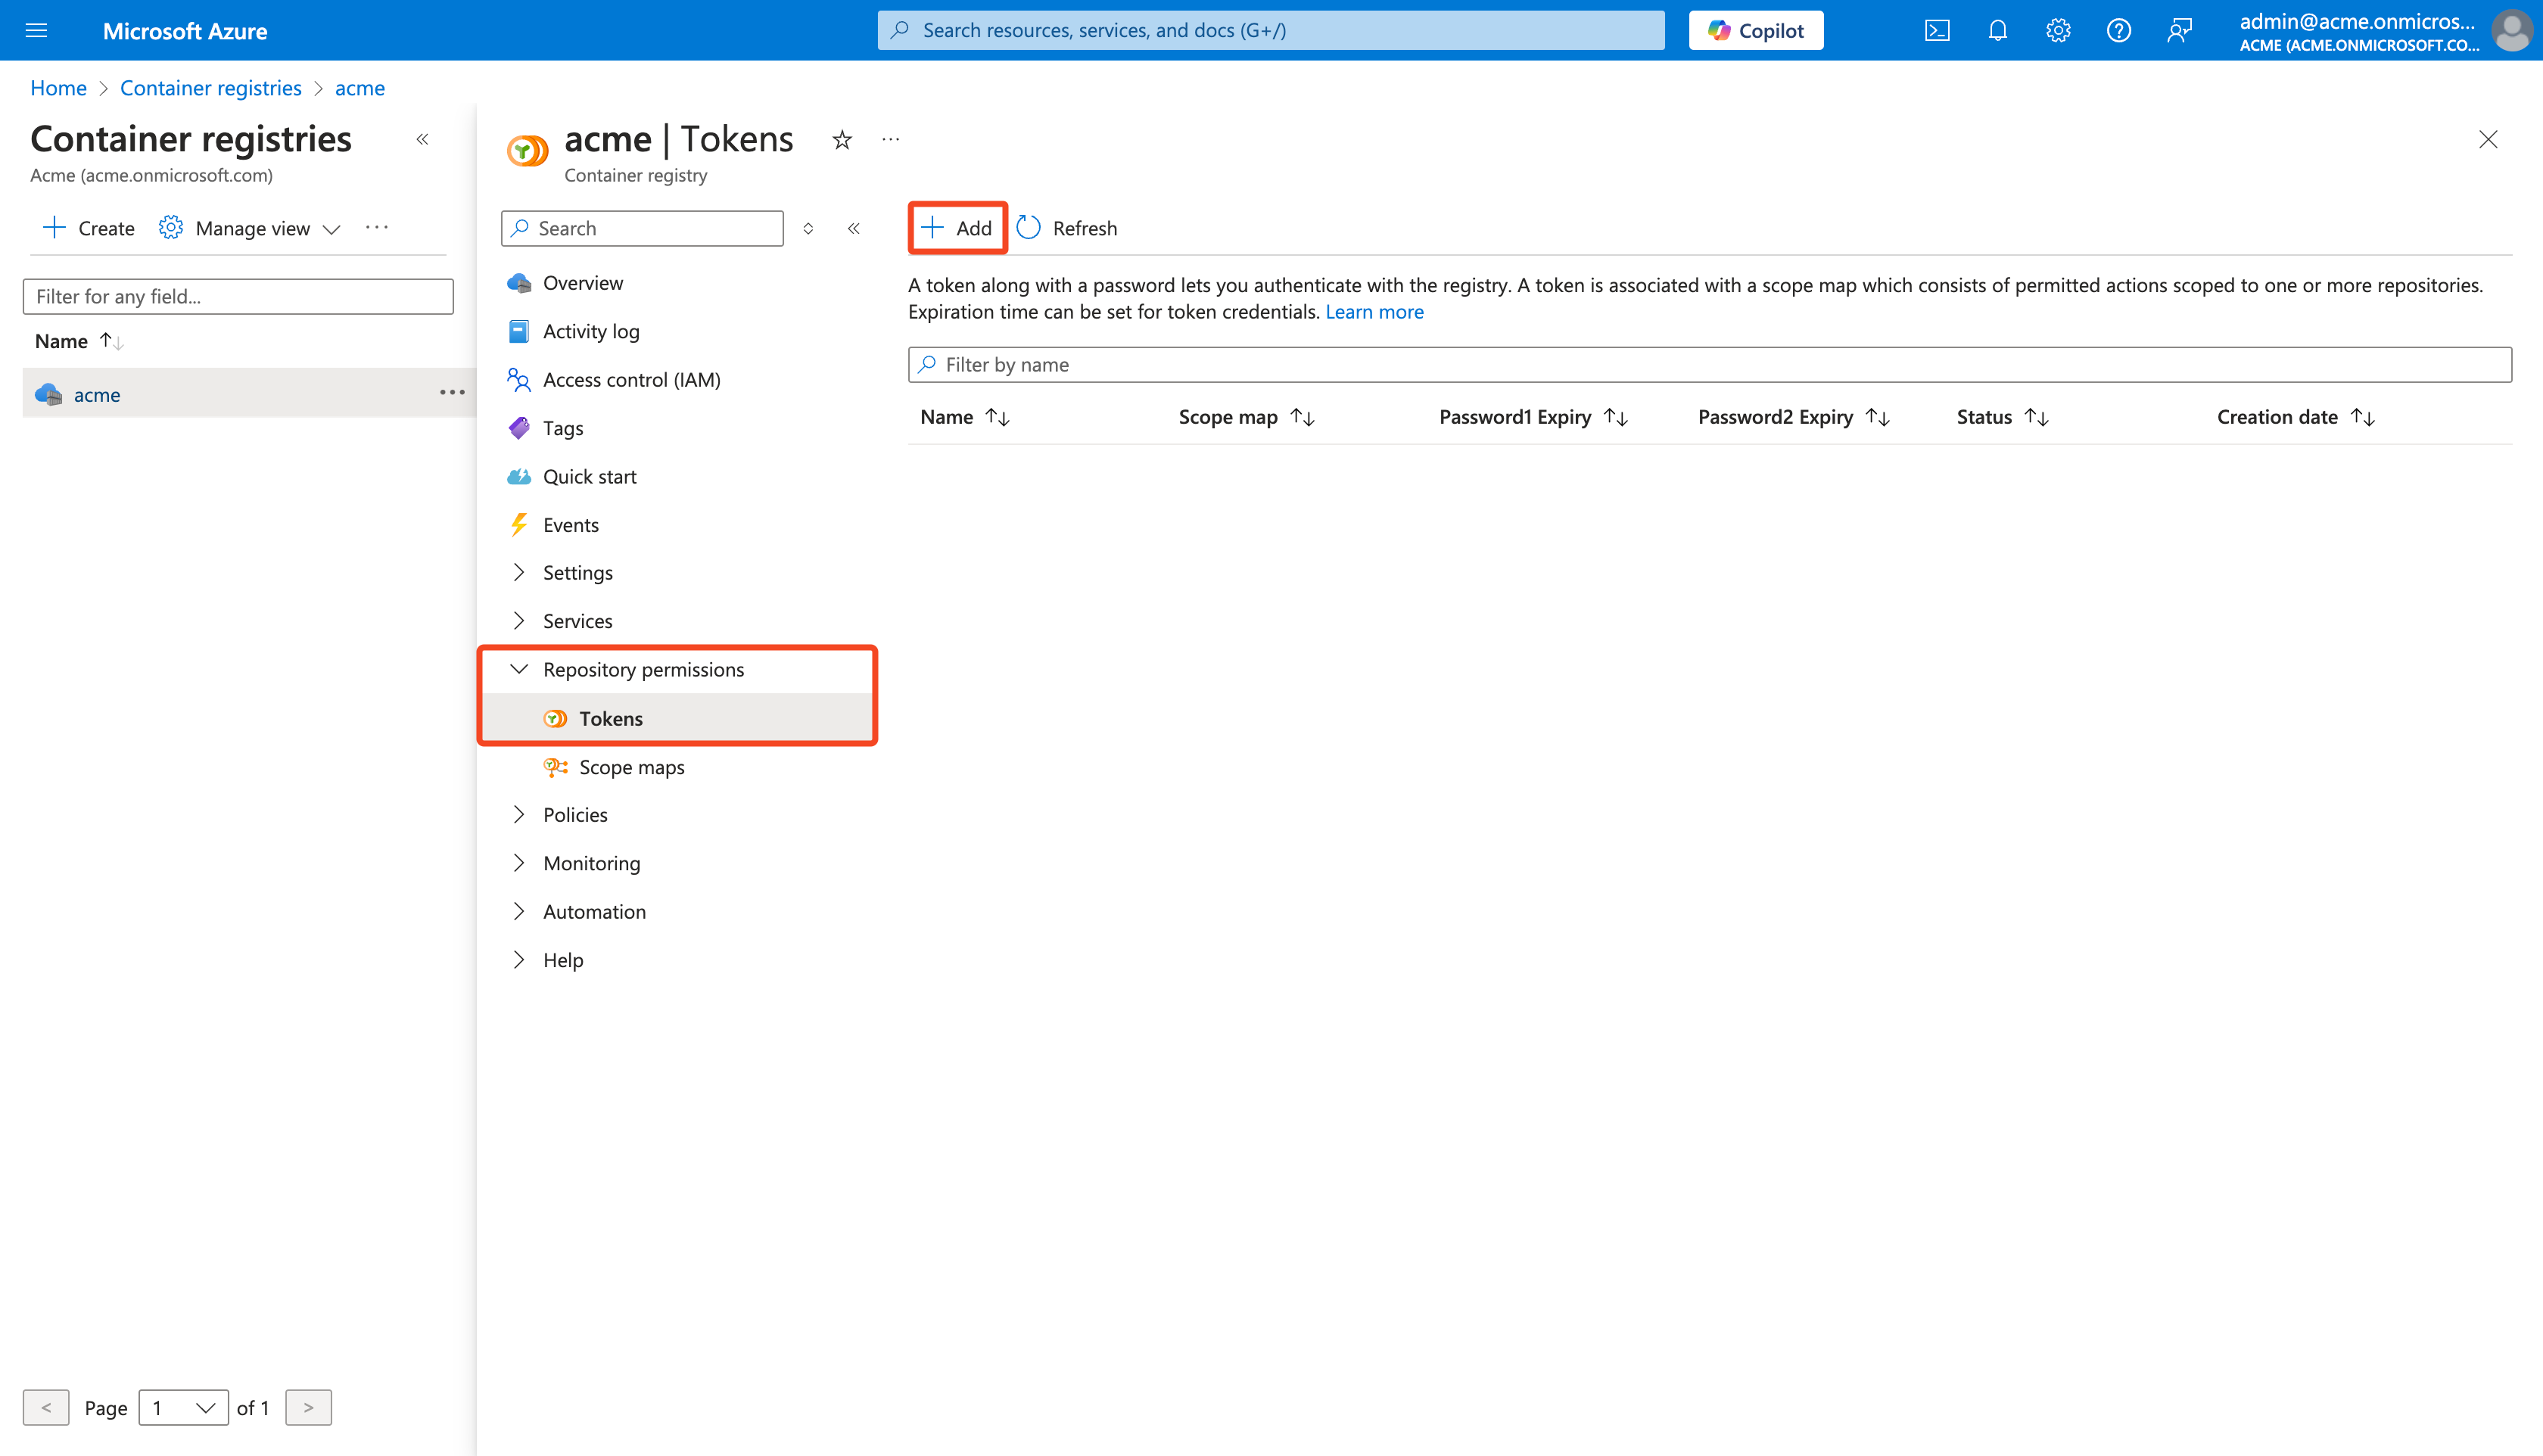
Go to the Repository permissions > Tokens section
-
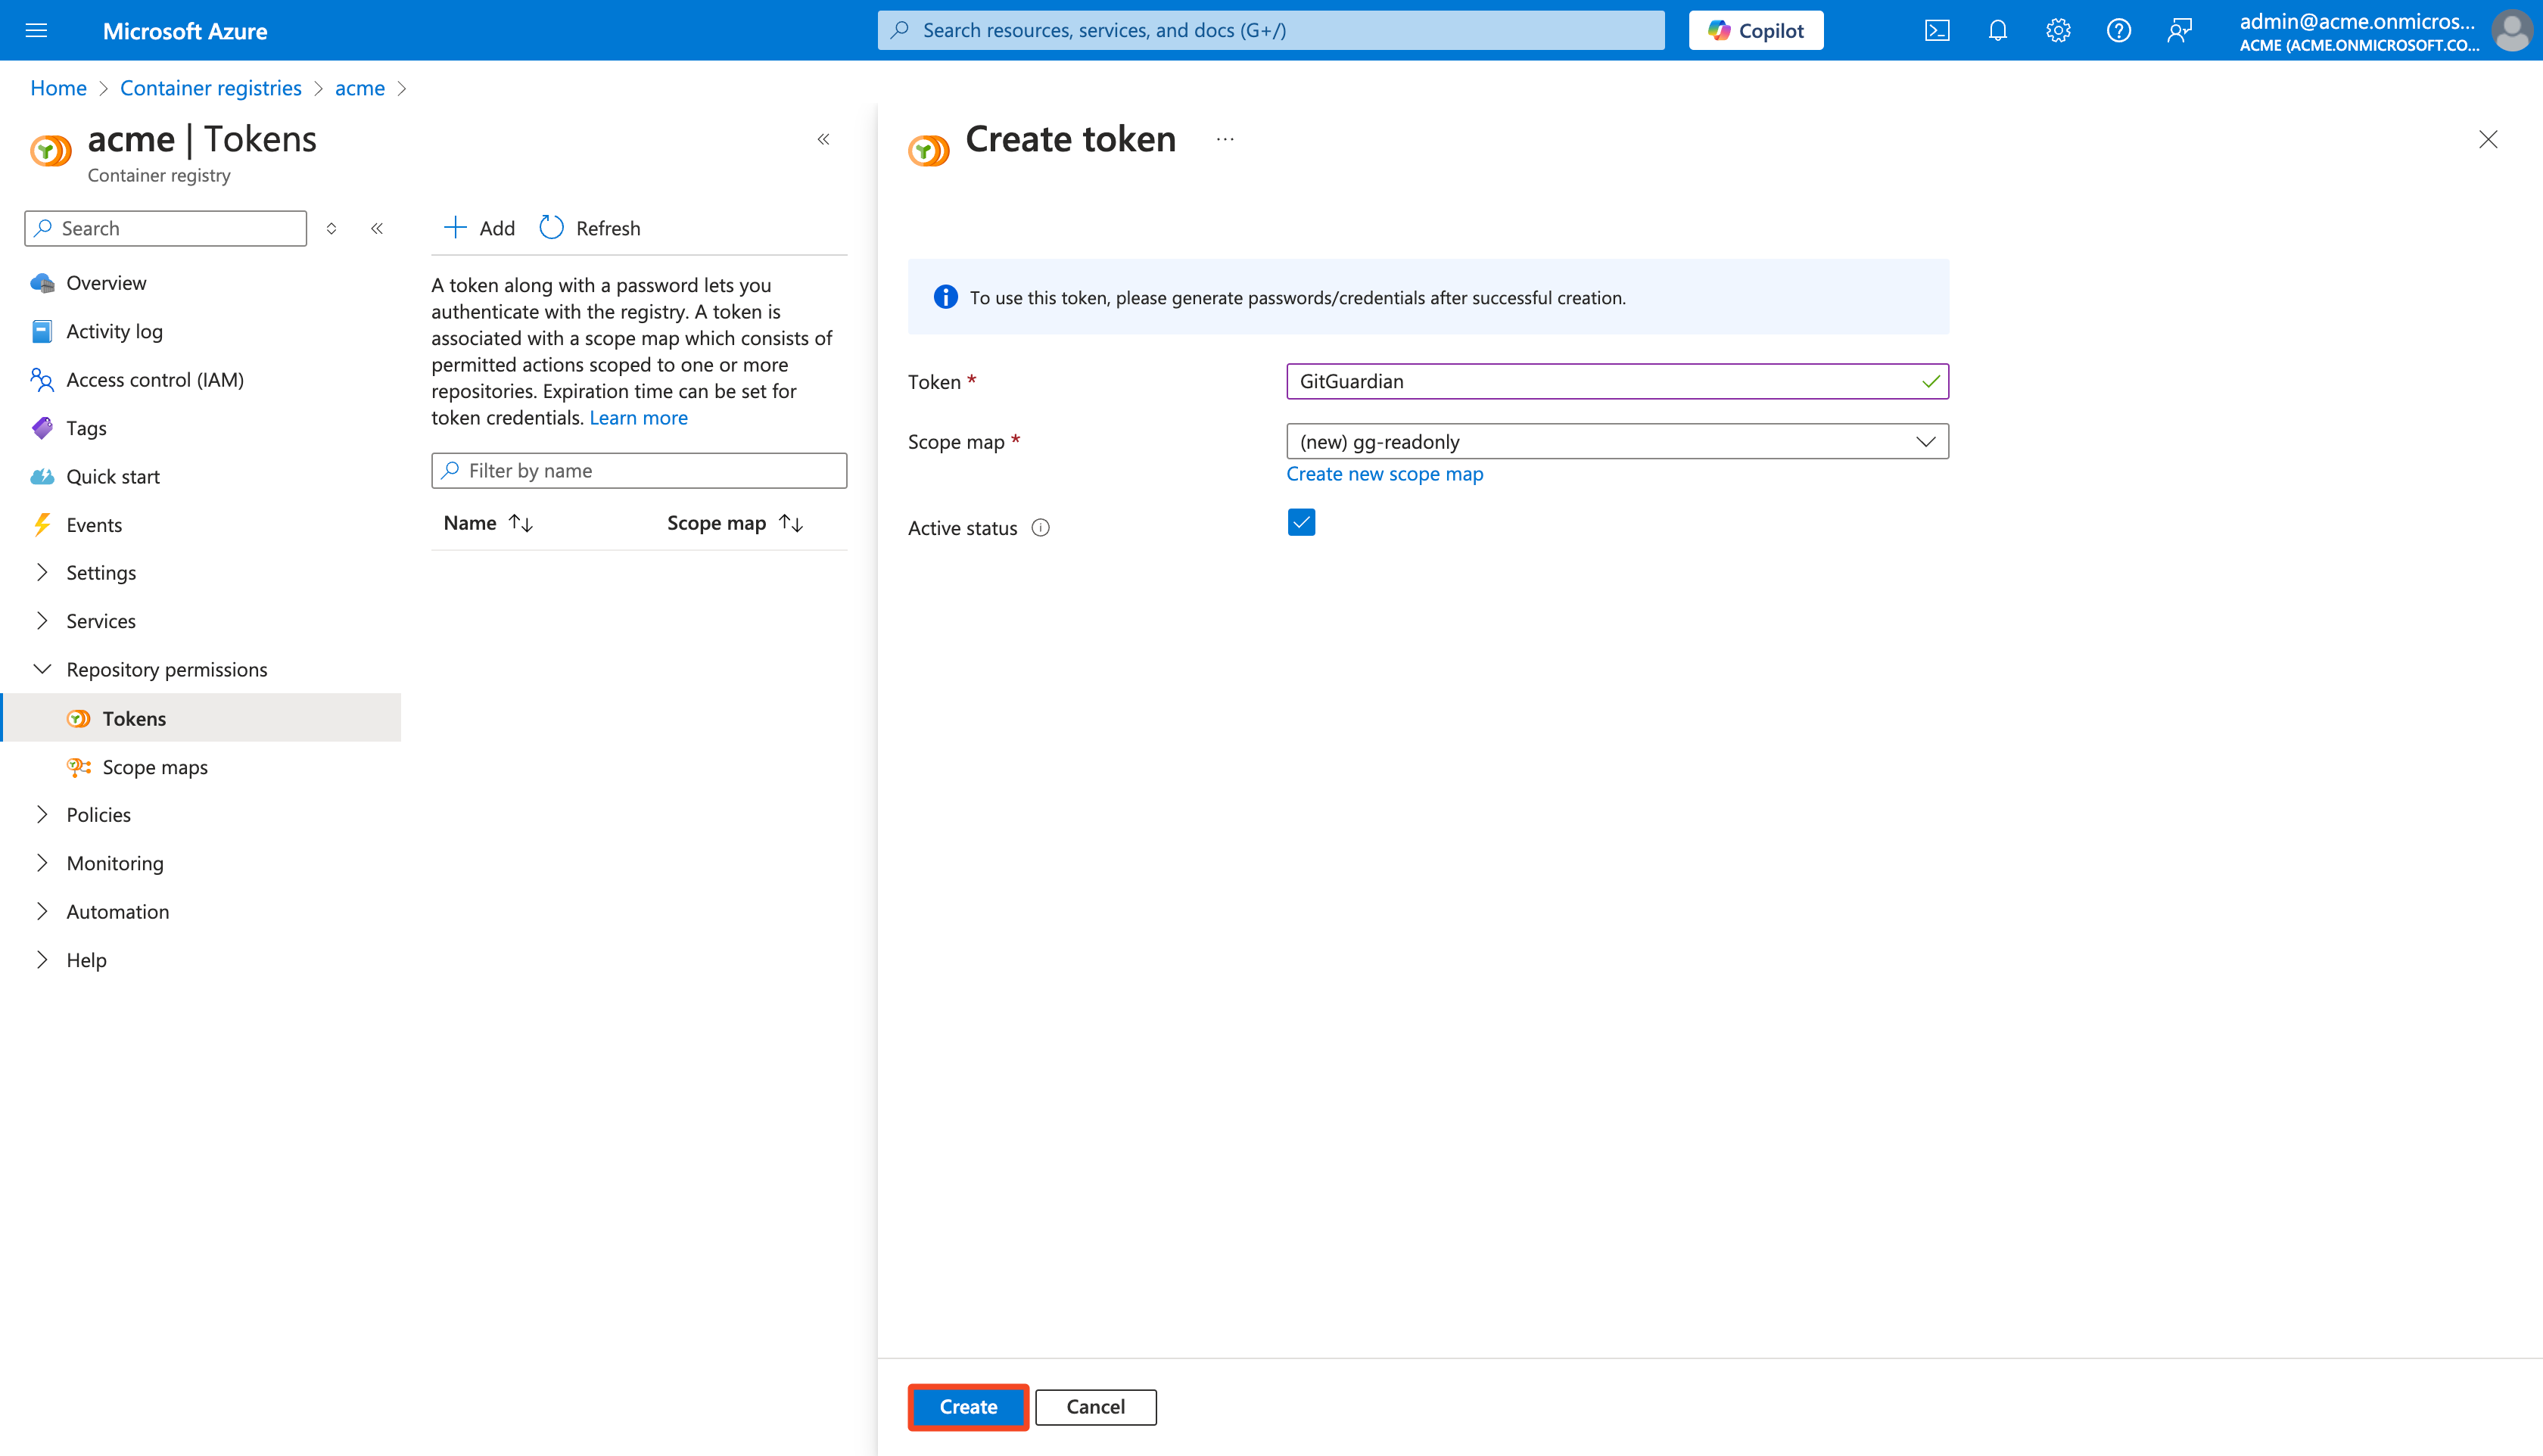
Click Add to create a new token
-
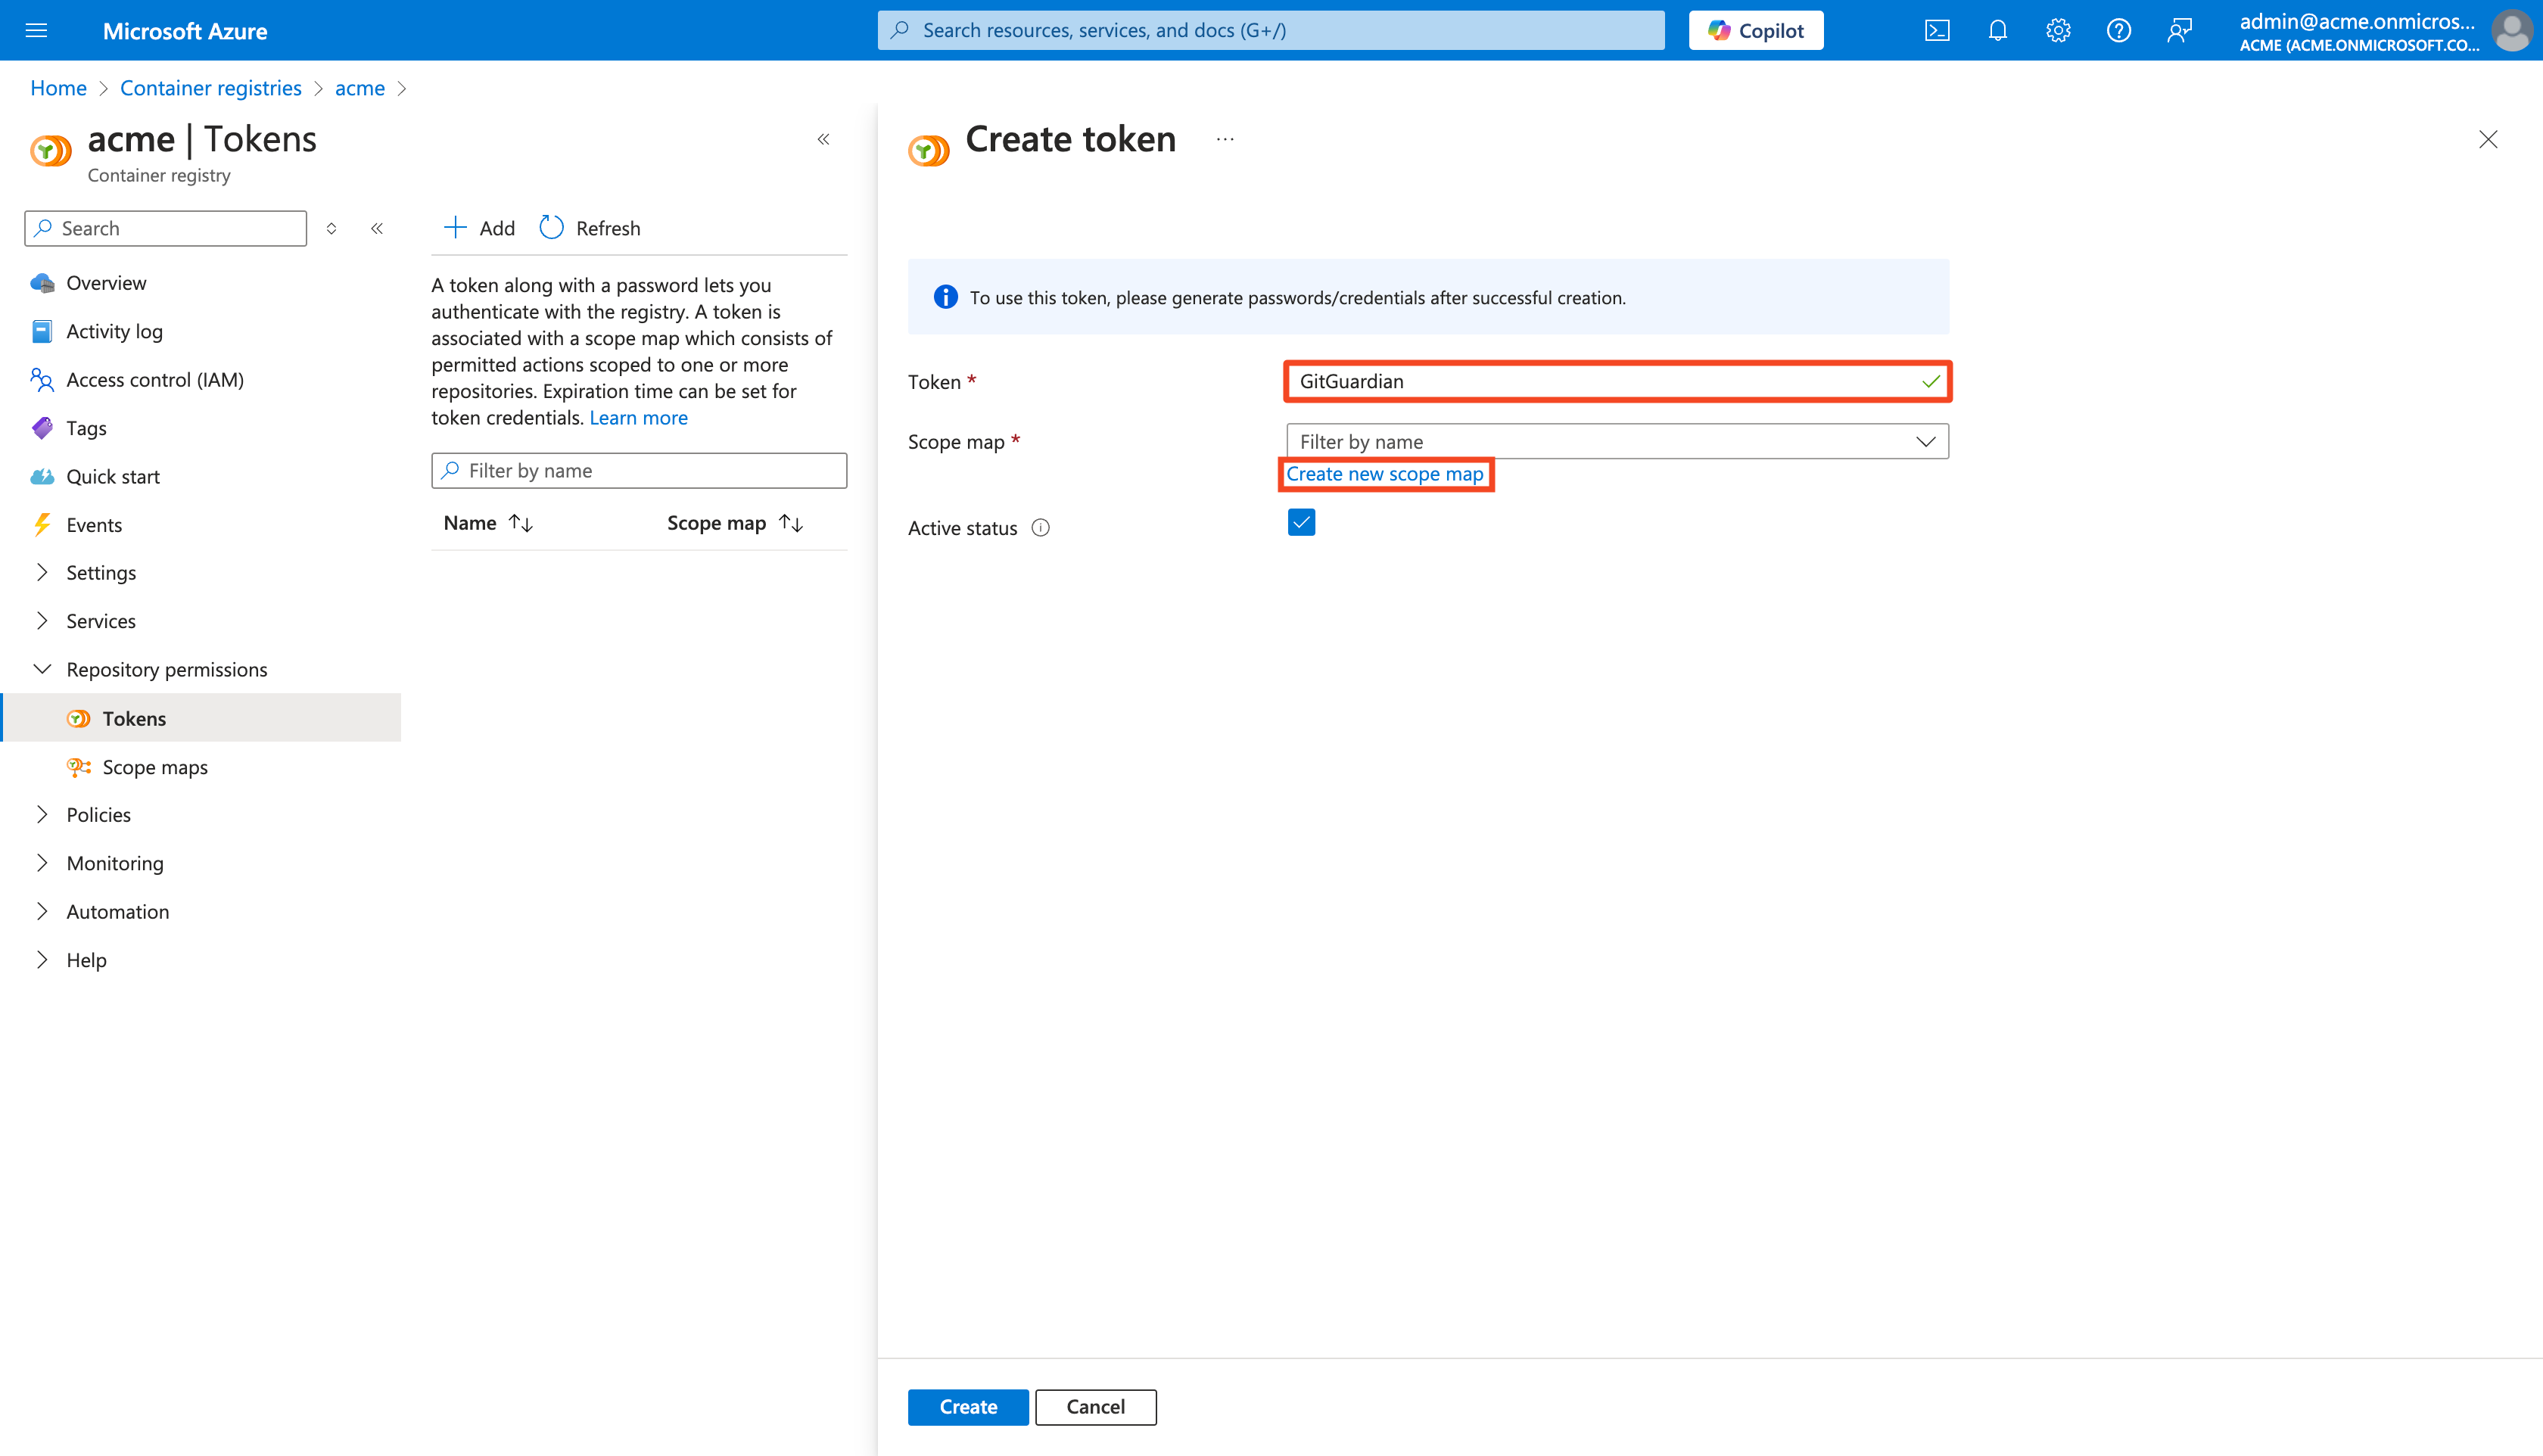
Provide a Token name:
GitGuardian -
Click Create new scope map
-
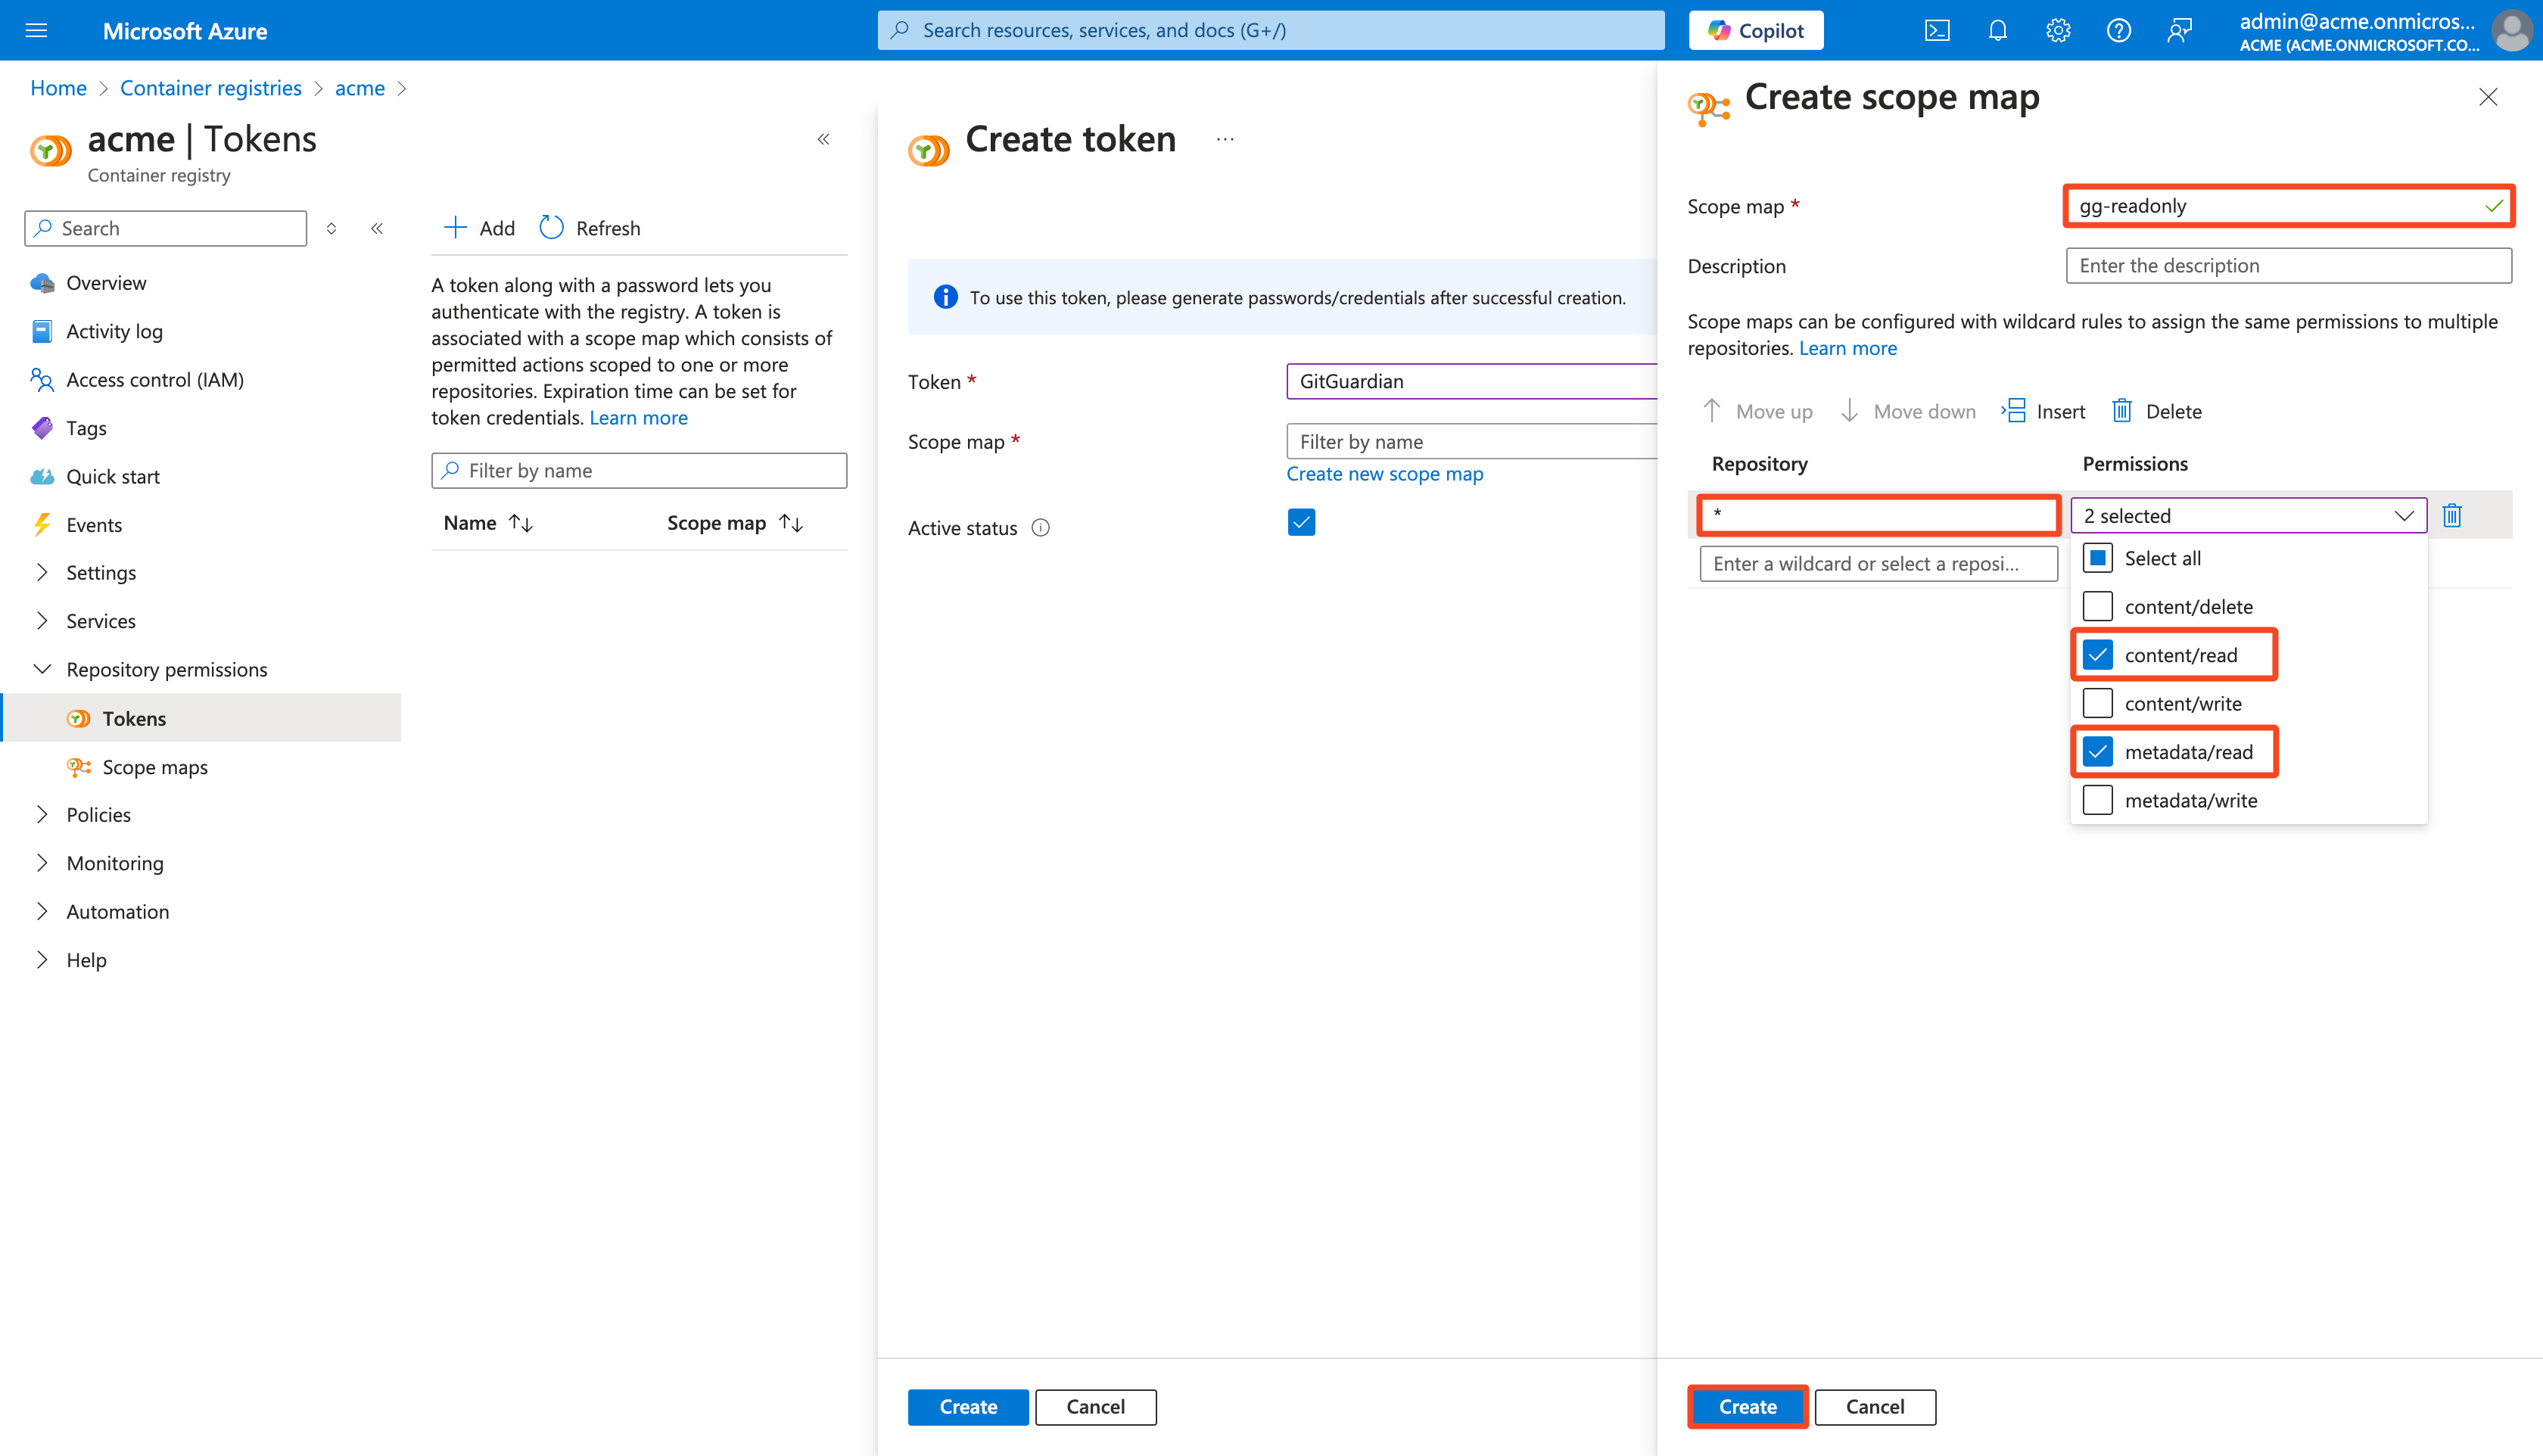
Name the Scope map (e.g.:
gg-readonly) -
Type
*in Repository to select them all -
Select
content/readandmetadata/readas Permissions -
Click Create to create the new scope map
-
Click Create to create the new token
-
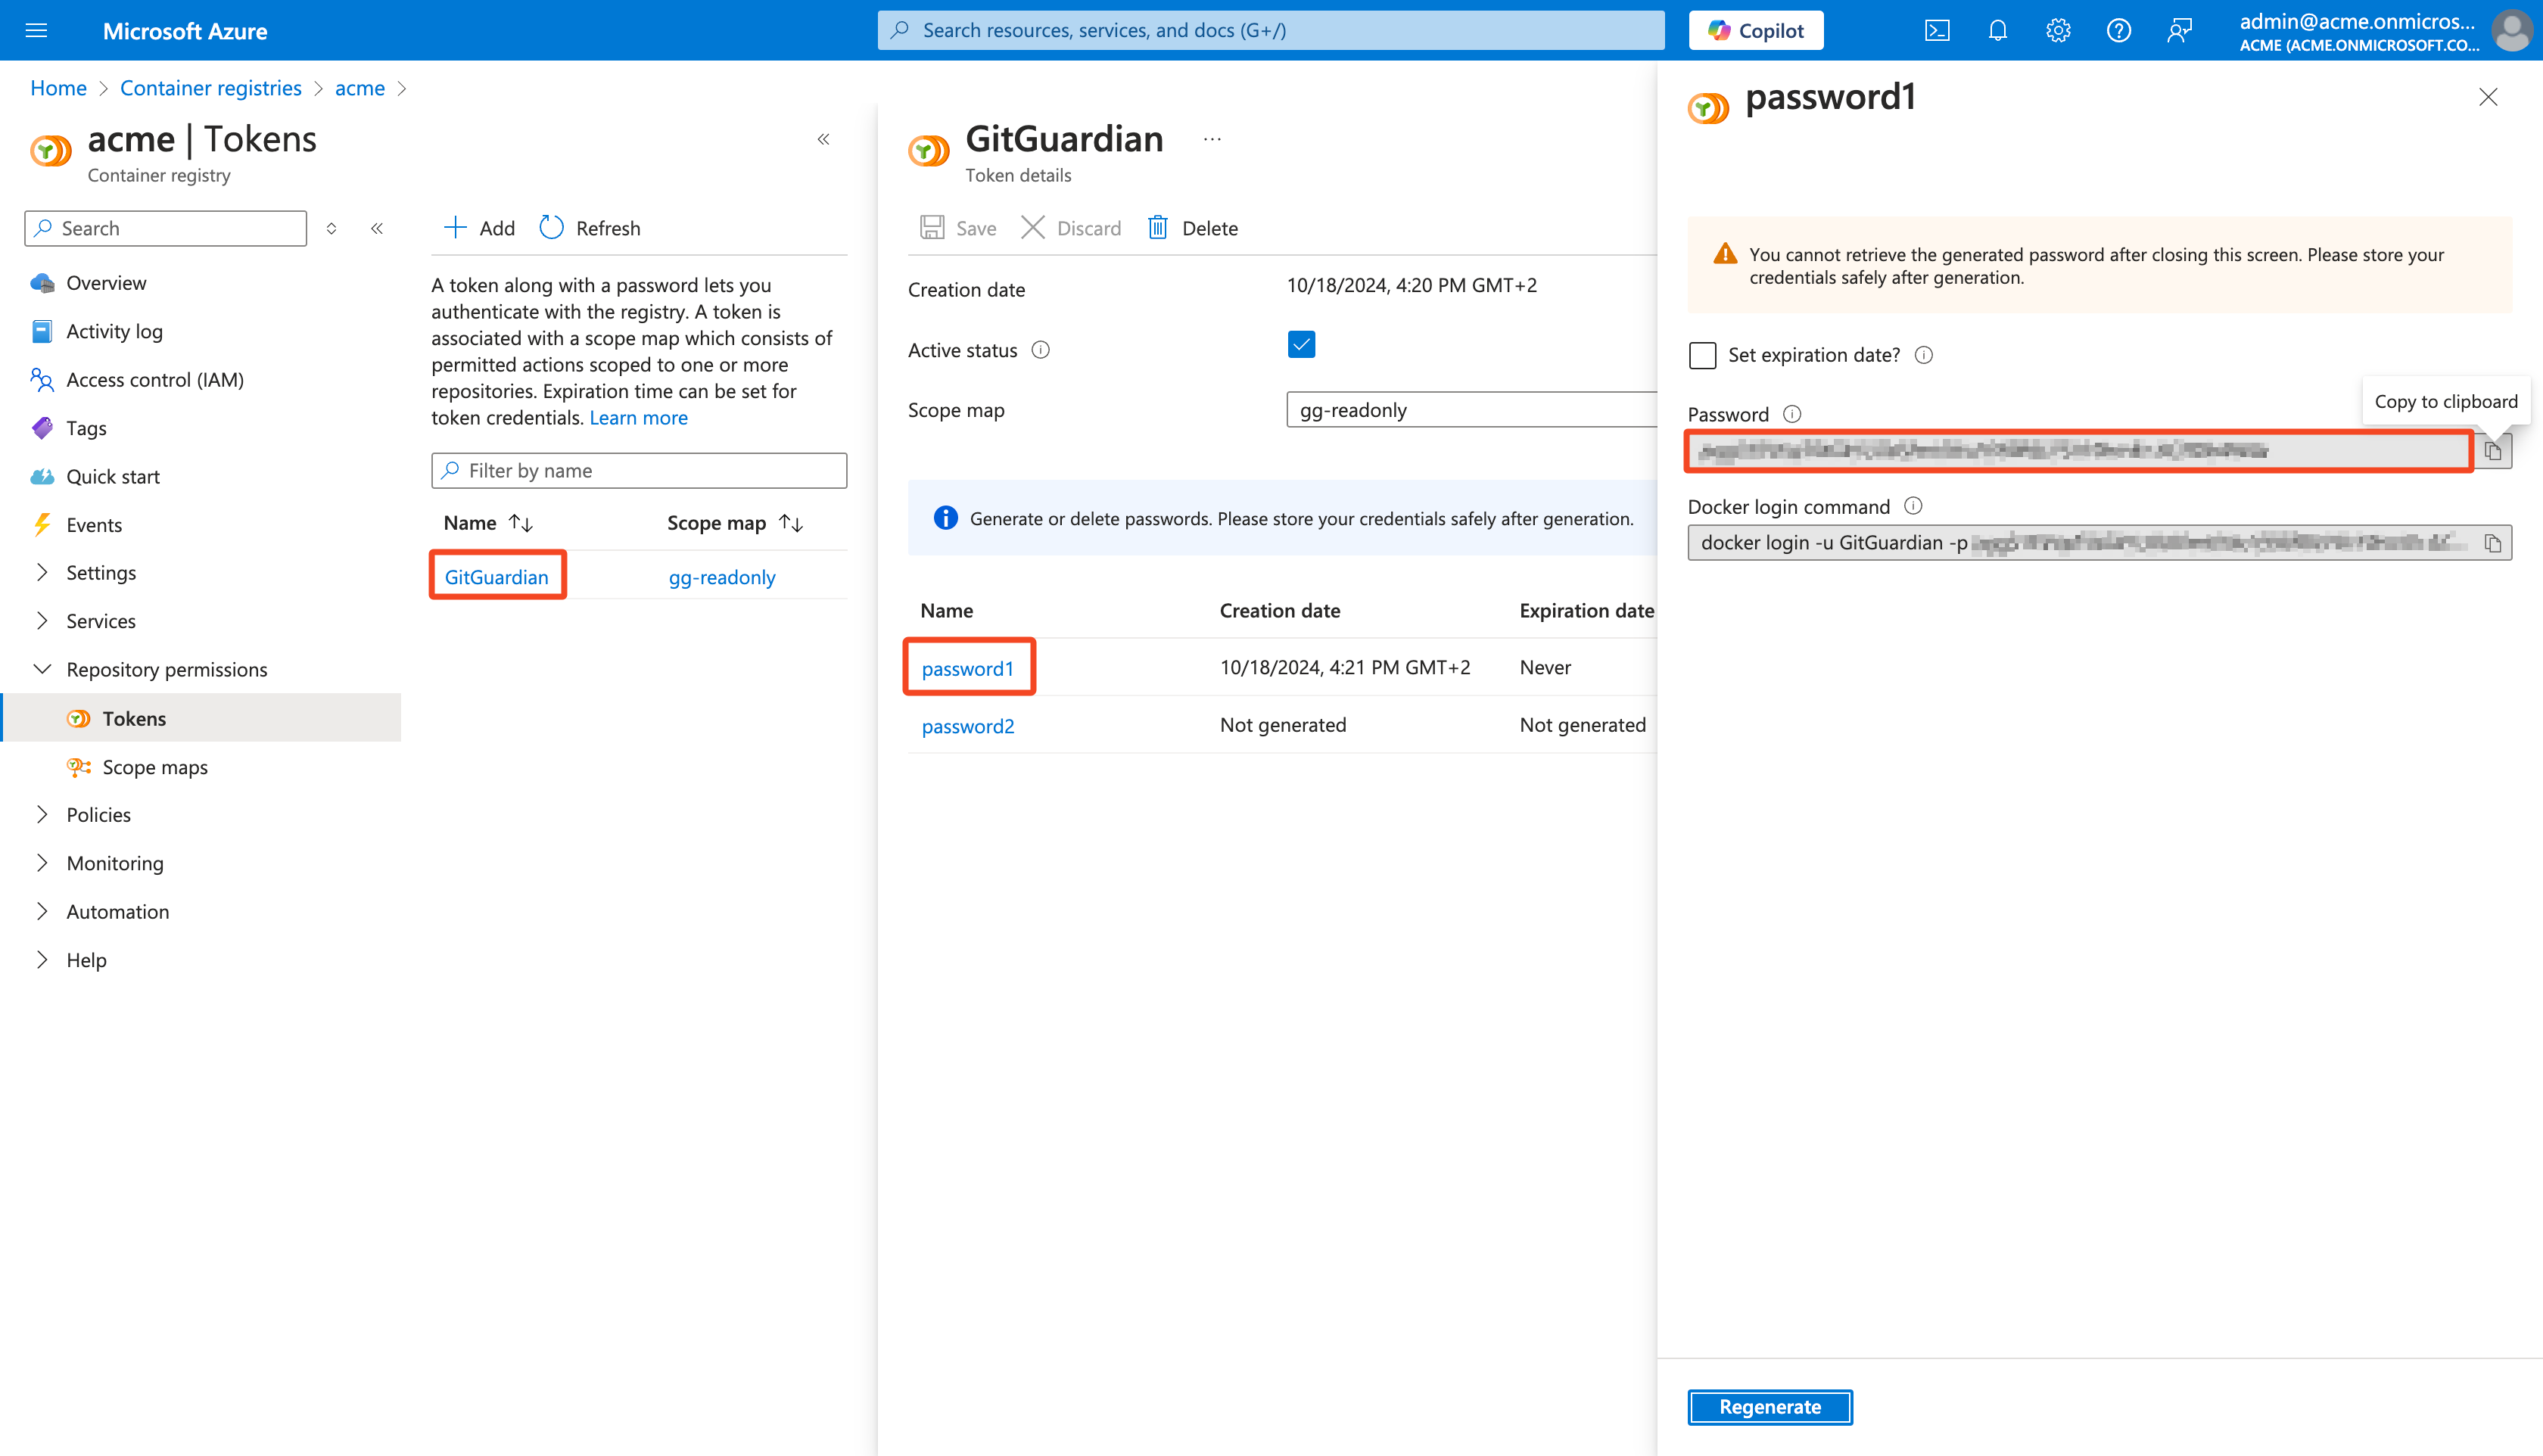
Select newly created Token
-
Click password1 (You have 2 passwords by default)
-
Click Generate to generate a new password
-
Copy the Password
-
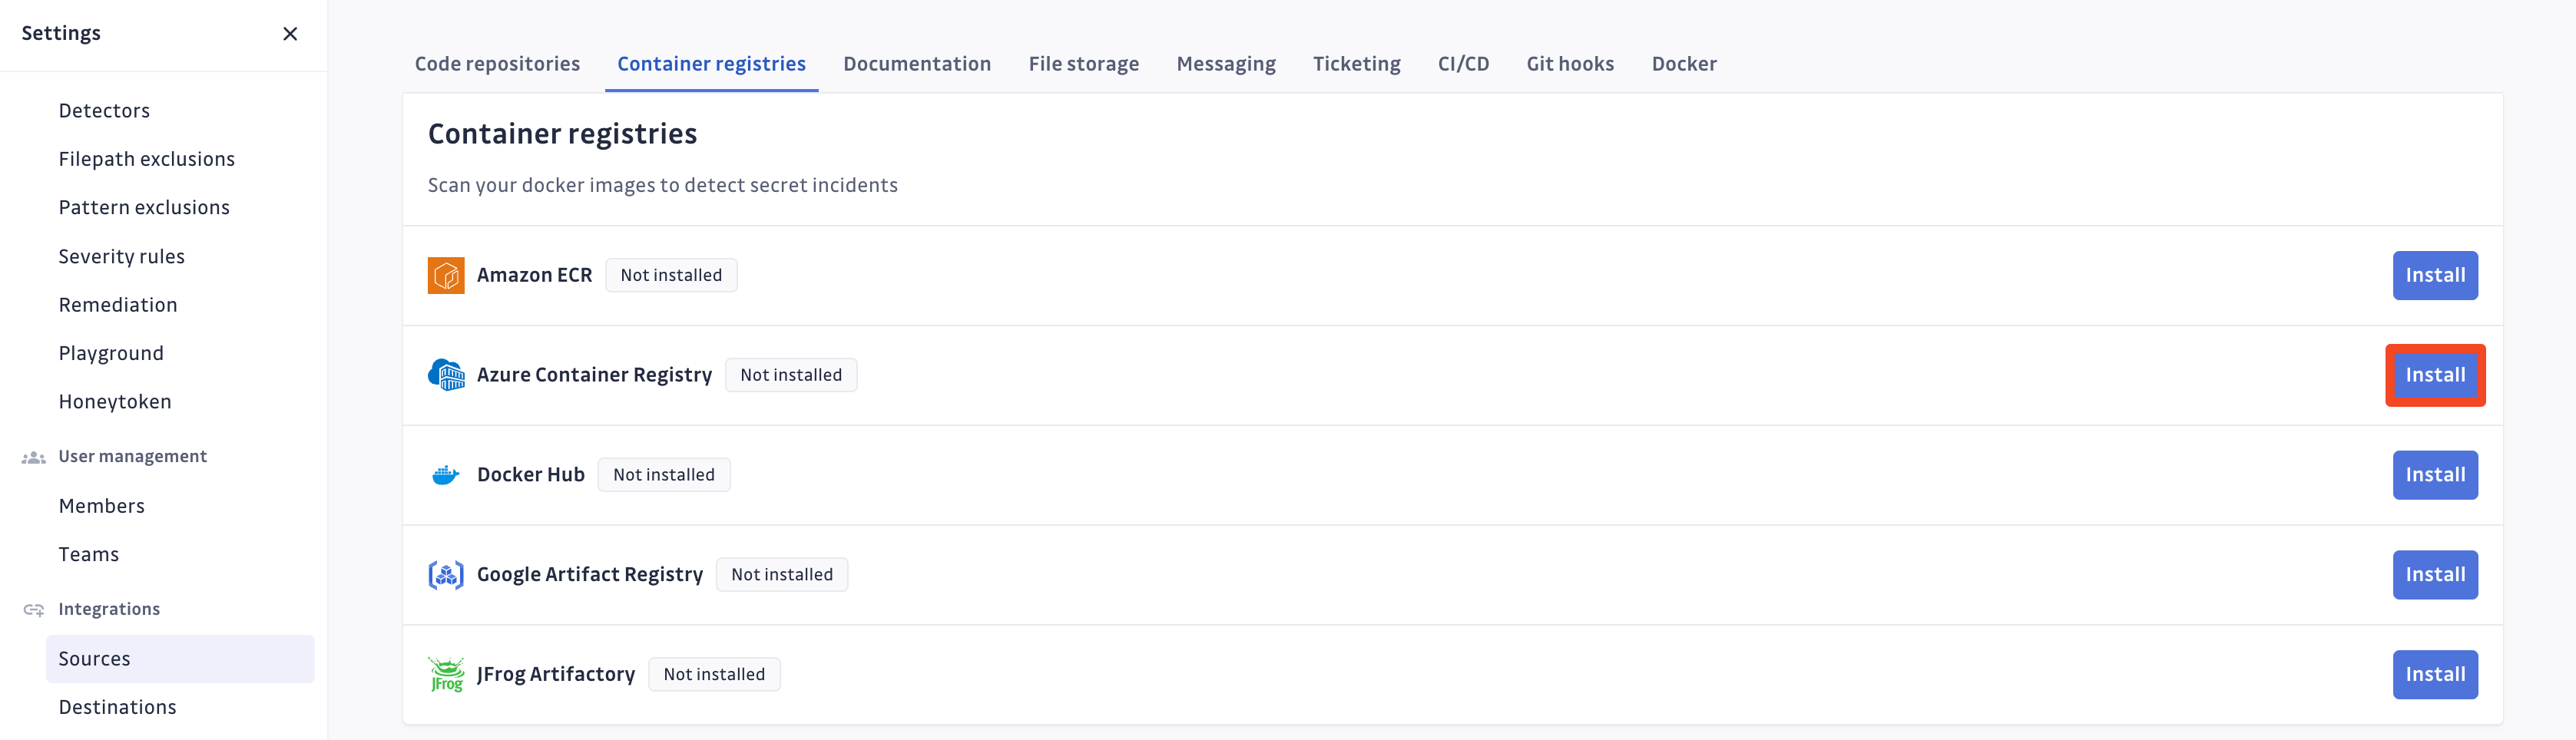
In the GitGuardian platform, navigate to the Sources integration page
-
Click Install next to Azure Container Registry in the Container registries section
-
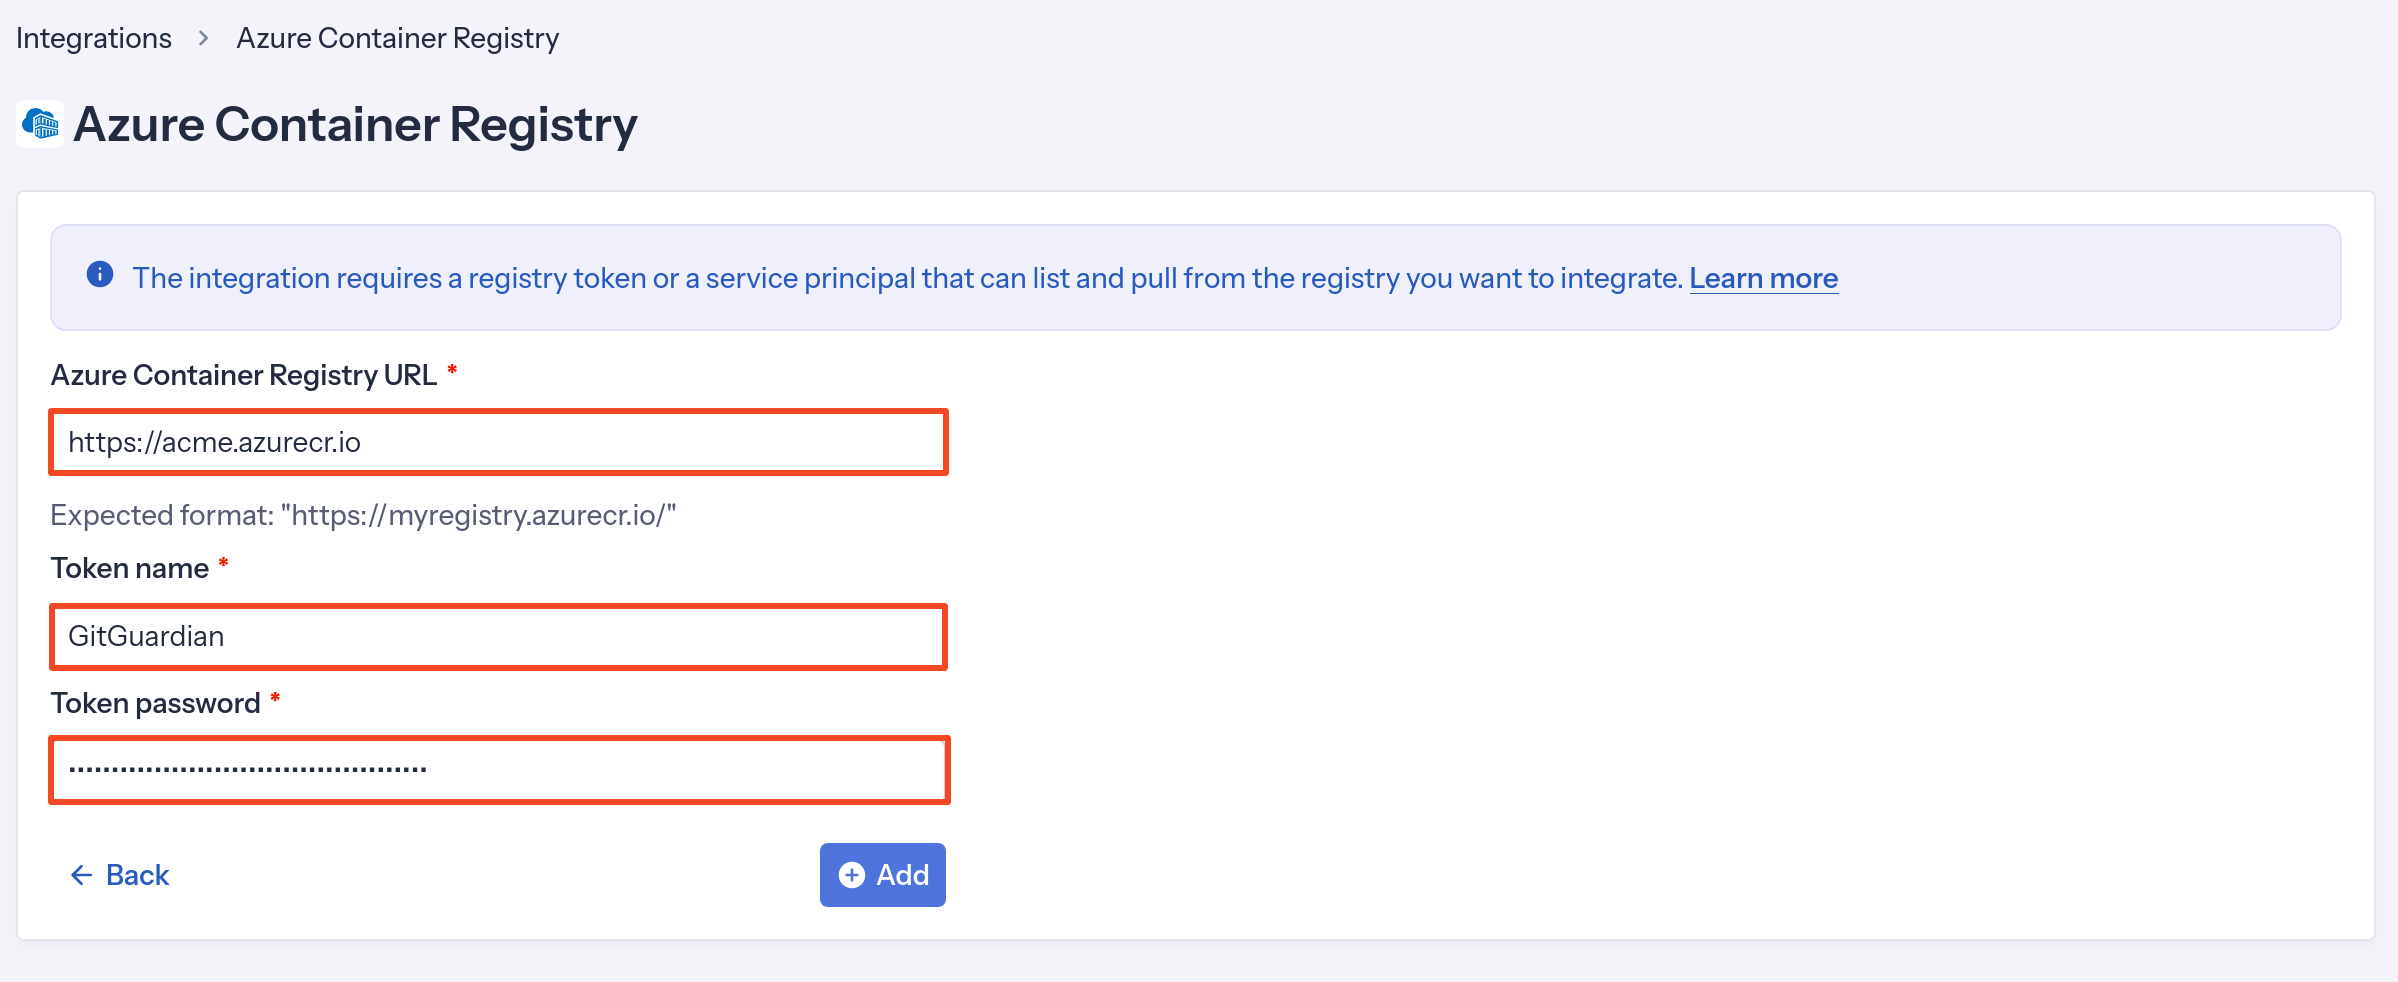
On the Azure Container Registry integration page, the installation form opens. If you already have installations, click Install to add another registry.
-
Paste your Login server (4) in the Azure Container Registry URL field, starting with
https://(e.g.:https://myregistry.azurecr.io/) -
Paste your Token name (7) in the Token name field
-
Paste your Password (17) in the Token password field
-
Click Add
-
In the Customize the monitored perimeter modal, choose what to monitor and click Ok, got it!:
- Monitor specific Azure Container Registry repositories (Recommended)
- No repositories are monitored by default, you will have to select them manually.
- Newly created repositories will not be monitored by default. You can adjust this setting at any time.
- Recommended to optimize your bandwidth costs.
- Monitor the entire Azure Container Registry registry
- All repositories are monitored by default with a full historical scan automatically triggered.
- Newly created repositories will be monitored by default. You can adjust this setting at any time.
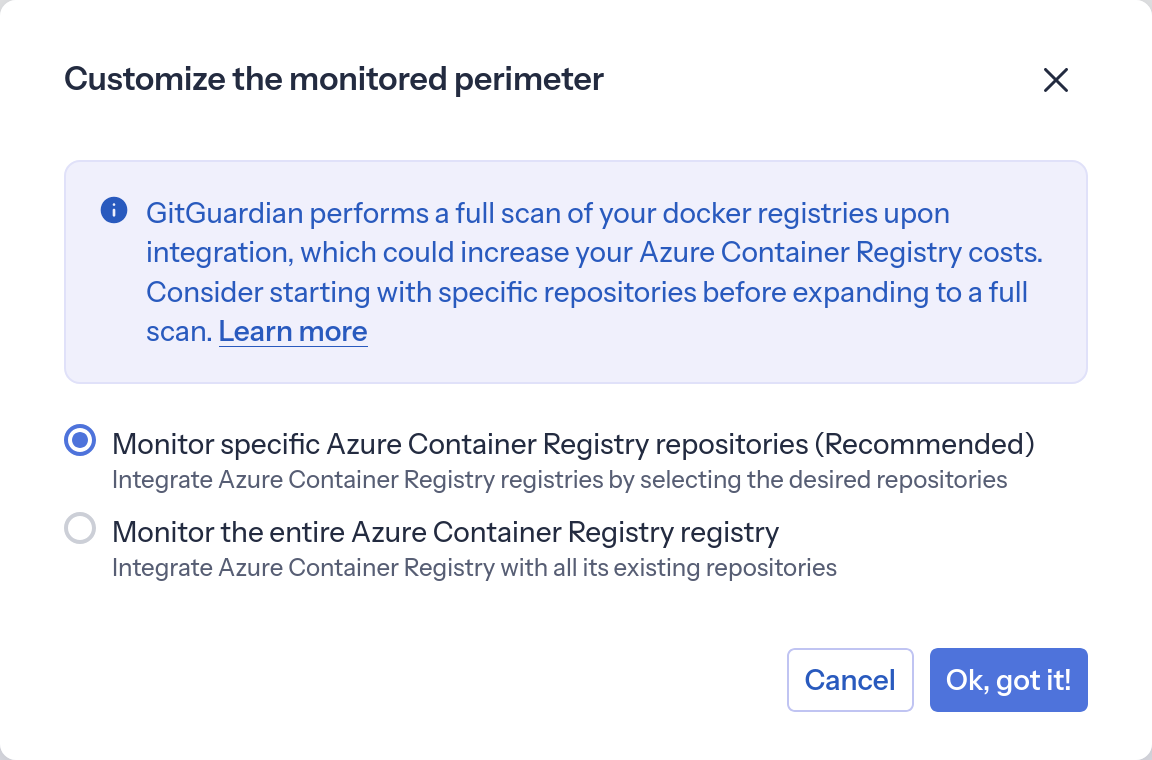
- Monitor specific Azure Container Registry repositories (Recommended)
That's it! Your Azure Container Registry instance is now installed, and GitGuardian is monitoring all Docker images of your selected repositories for secrets.
Customize your monitored perimeter
To customize the monitored repositories, navigate to your Azure Container Registry settings.
- In the Sources table, select the repositories to include or exclude
- Click Monitor or Unmonitor
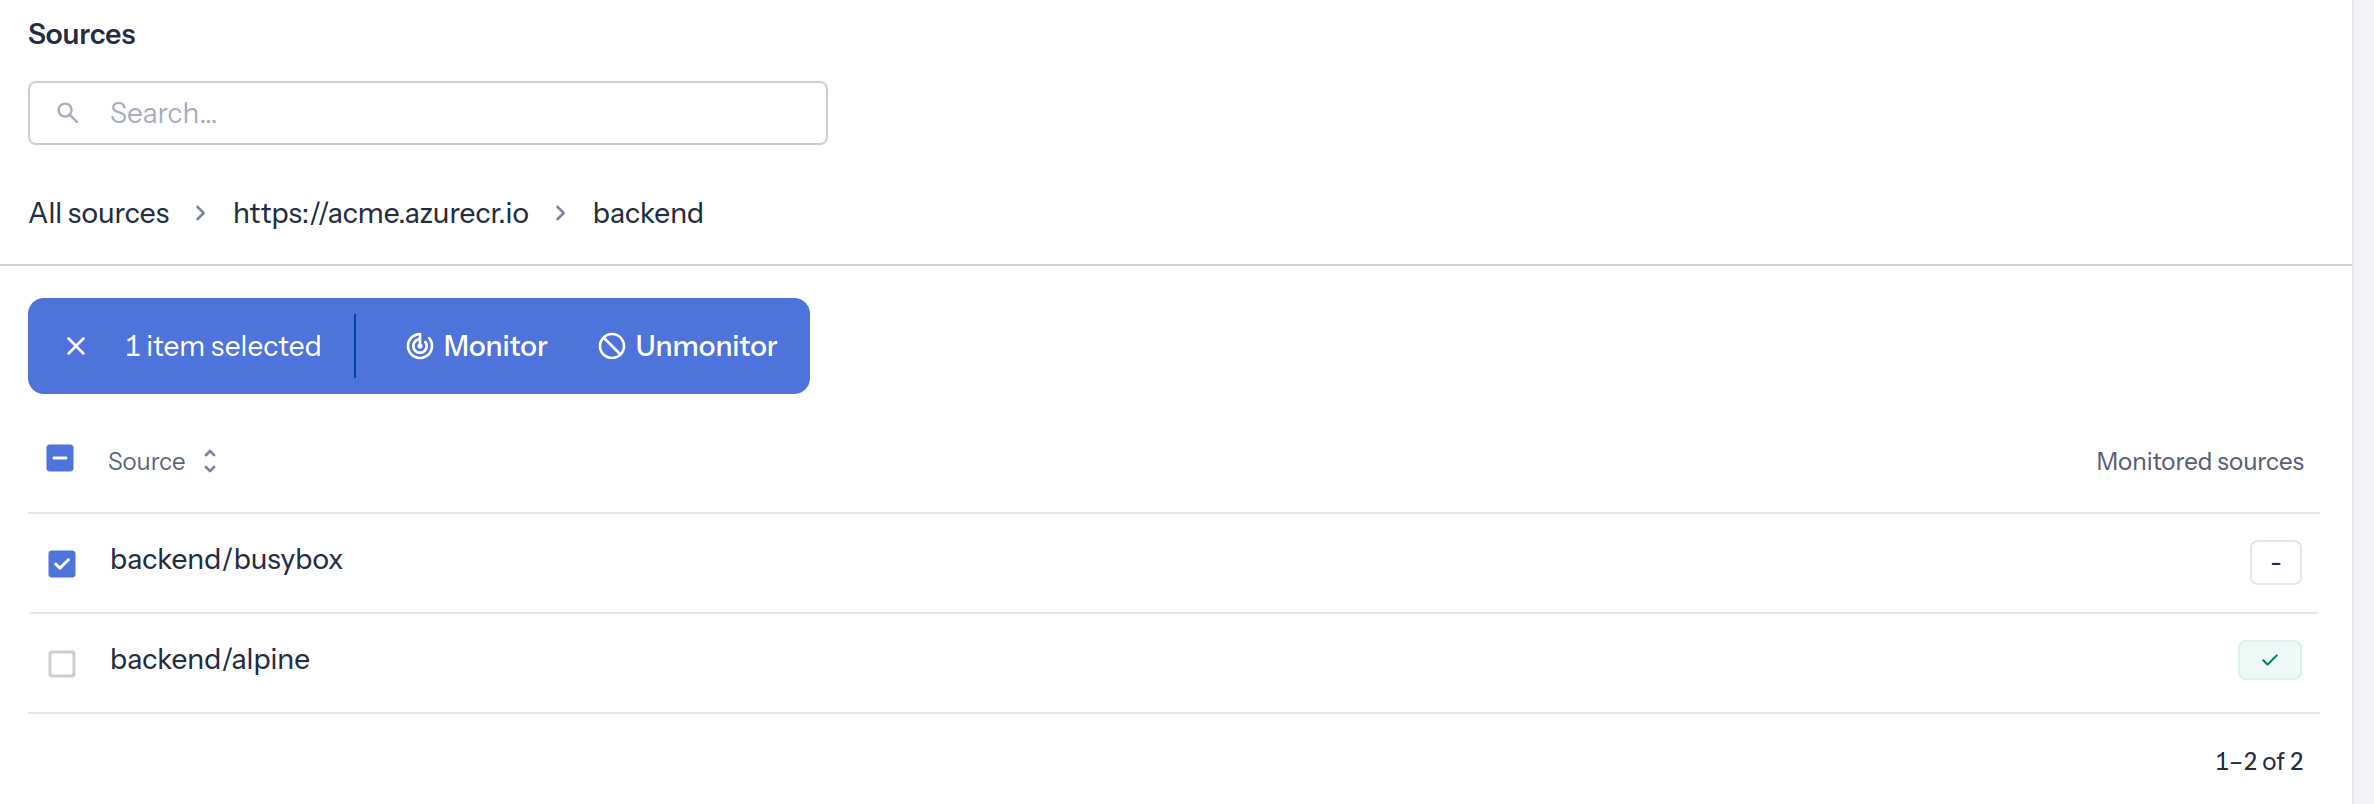
Repositories are grouped by registry, then by namespace: team/app/api sits in the team > app folder. If you rename a namespace in Azure, GitGuardian sees the repository as a new source. The old source is removed from your perimeter but keeps its incidents.
Automatic repository monitoring
You can enable or disable the automatic addition of newly created repositories to your monitored perimeter with the Automatically monitor new repositories toggle in your Azure Container Registry settings.
Troubleshoot an installation
The Installations table in your Azure Container Registry settings shows the Status of each registry. When a registry is unhealthy, click Troubleshoot to see the cause, then:
- Click Check again for temporary issues, such as network errors or rate limiting
- Click Update credentials when the token is no longer valid or can no longer list and pull from the registry, and enter a new Token name and Token password
Understanding scanning capabilities
Historical scanning
Uncover your secret debt: When you first integrate this source, GitGuardian performs a comprehensive scan of your entire content history, based on your customized perimeter. This reveals secrets that may have been exposed weeks, months, or even years ago - helping you address your existing security debt.
How to trigger a historical scan: Go to your perimeter page, select the sources you want to scan, and click Scan in the bulk actions bar. See Manage your monitored perimeter for plan-based size limits, error handling, and full details.
Incremental scanning
Stay protected with regular monitoring: Once integrated, GitGuardian provides ongoing protection through scheduled automated scans of your content. New and modified content is systematically monitored at regular intervals, ensuring comprehensive coverage and timely detection of any secret exposures. Your source remains under GitGuardian's protection, giving you confidence that secrets won't go unnoticed.
Uninstall your Azure Container Registry instance
To uninstall an Azure Container Registry instance:
- Navigate to your Azure Container Registry settings
- In the Installations table, click the bin icon next to the registry to uninstall
- Confirm by clicking Yes, uninstall in the confirmation modal
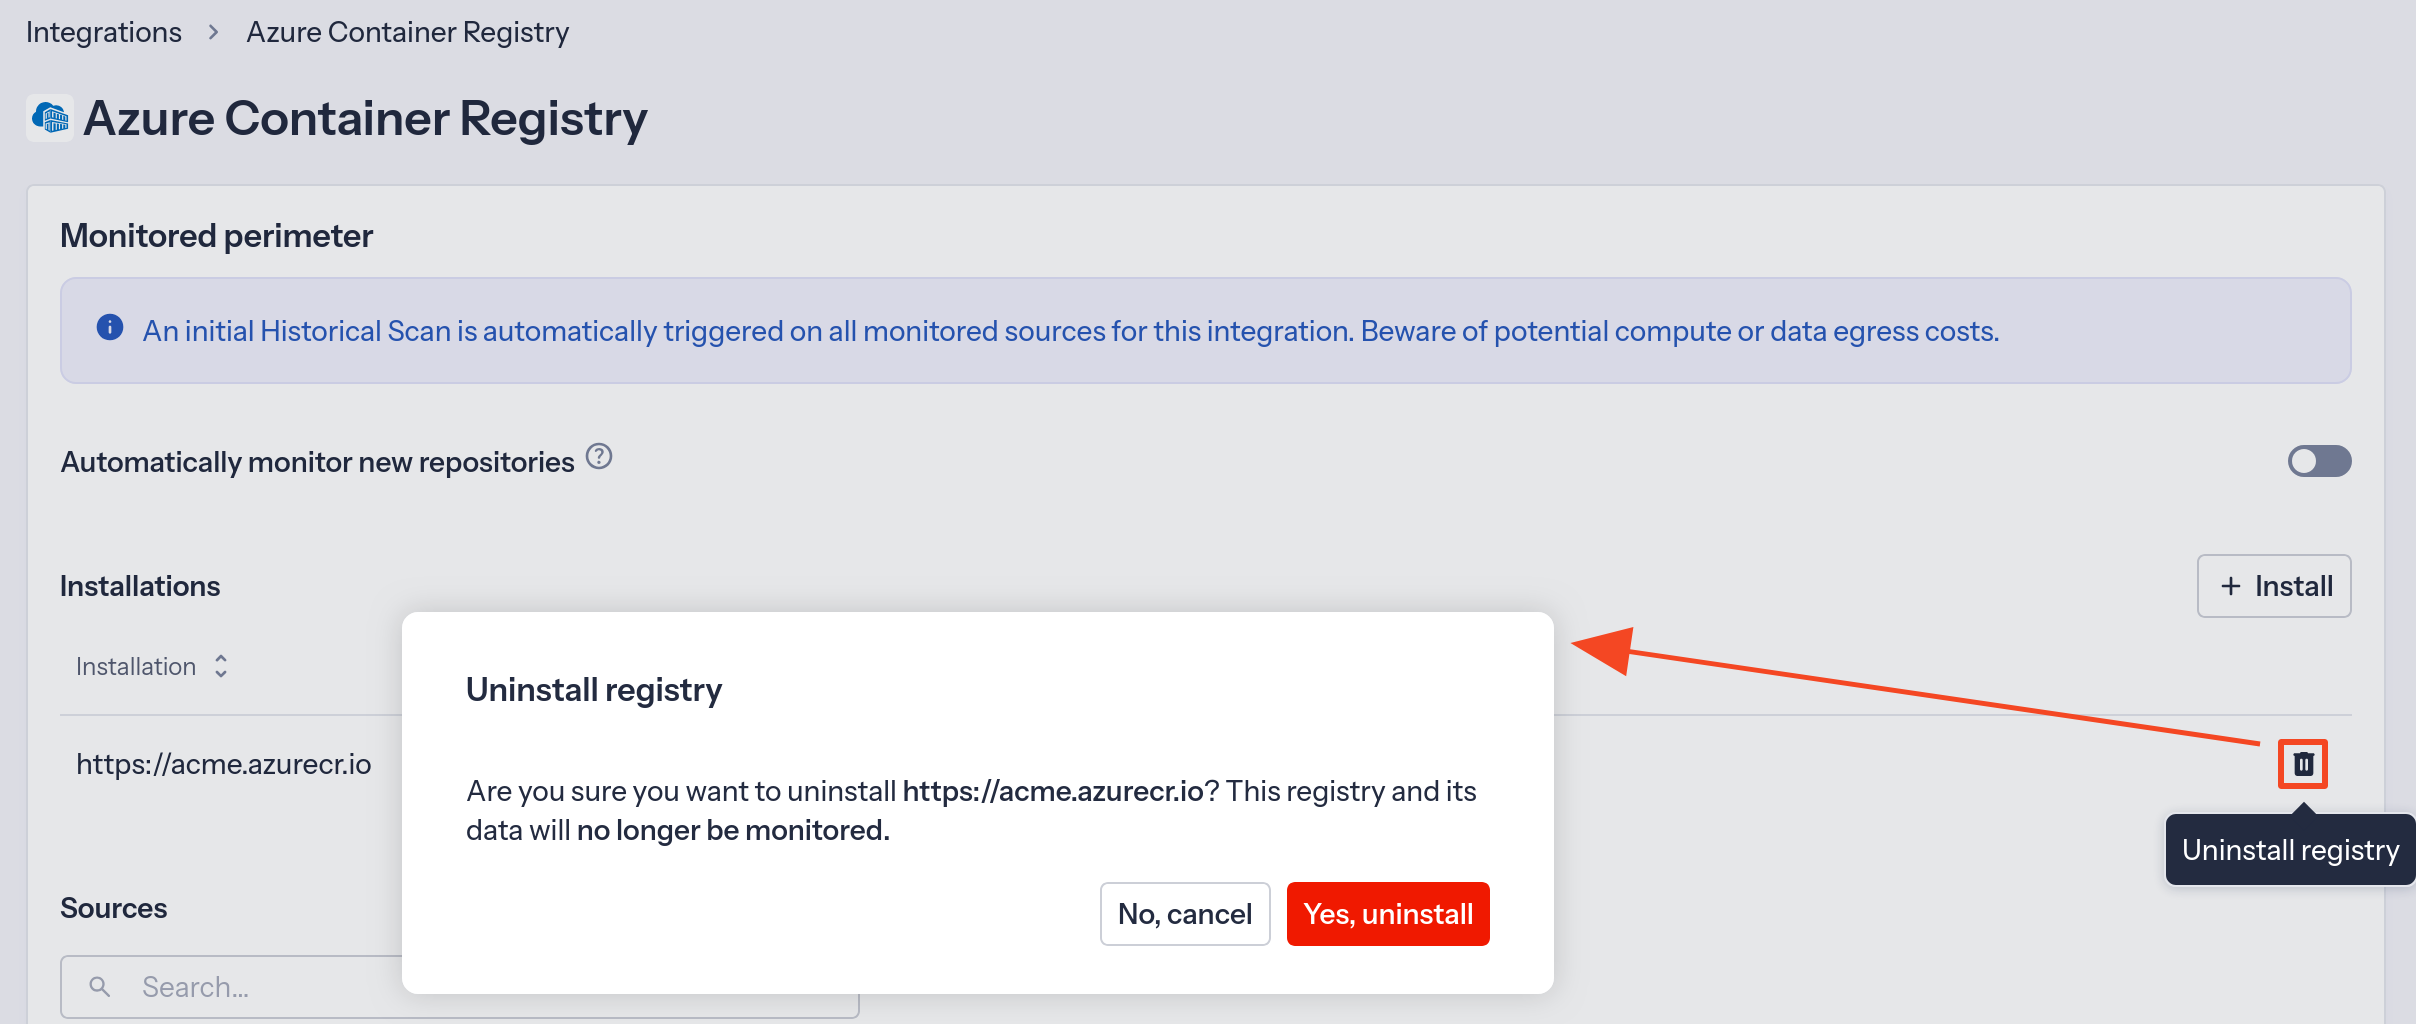
That's it! Your Azure Container Registry instance is now uninstalled.
Excluded paths
GitGuardian automatically excludes files from scanning if their paths contain any of these regular expressions:
/__pypackages__/
/\.venv/
/\.tox/
/site-packages/
/venv/
distutils/command/register\.py
python.*/awscli/examples/
python.*/dulwich/(tests|contrib/test_)
python.*/hgext/bugzilla\.py
python.*/mercurial/util\.py
python.*/test/certdata/
python.*/urllib/request\.py
python.*/pygments/lexers/
/cryptography.+/tests/.+(fixtures|test)_.+\.py
/python.+pygpgme.+/tests/
botocore/data/.+/(examples|service)-.+\.json
usr(/local)?/lib/python.+/dist-packages
/libevent.+/info/test/test/
/conda-.+-py.+/info/test/tests.+/test_.+\.py
/python[^/]+/test/
/man/man5/kdc\.conf\.5
erlang.*(inets|ssl).*/examples/
/gems/.*httpclient.*/(test|sample)/
/gems/.*faraday.*/
/vendor/bundle/
/\.gem/
ruby-[^/]+/test/openssl/
/(g|G)o/src/cmd/go/internal/.*_test\.go
/(g|G)o/src/cmd/go/internal/.*/testdata/
/(g|G)o/src/cmd/go/testdata/
/(g|G)o/src/crypto/x509/platform_root_key\.pem
/(G|g)o/src/crypto/(tls|x509)/.*_test\.go
/(g|G)o/src/net/(url|http)/.*_test\.go
src/github.com/DataDog/datadog-agent/.*test.*\.go
google/internal/.*_test\.go
golang.org.*oauth2@.*/.*\.go
/flutter/.*/packages/flutter_tools/test/data/
/flutter/.*/examples/image_list/lib
/\.pub-cache
etc/ssl/private/ssl-cert-snakeoil\.key
perl.*Cwd\.pm
ansible/.*/tests/(integration|unit)/
ansible/.*/test/awx
ansible/collections/ansible_collections/.*/plugins/
/curl/.*/(tests|docs|lib/url\.c)
/doc/wget.+/NEWS
dist/awscli/examples/
usr(/local)?/lib/aws-cli/examples/
/google-cloud-sdk/(lib|platform)/
\.git/modules/third[-_]?party/
\.git/modules/external/
/\.npm/_cacache
/node_modules/
/\.parcel-cache/
/\.yarn/cache/
/\.m2/
/\.ivy2/cache/
/\.mix/
/\.hex/
/composer/cache/
/\.nuget/packages/
/libgpg-error/errorref\.txt
/Homebrew/Library/Taps/
/tcl[^/]+/http-.+\.tm
/tcl[^/]+/[^/]+/http-.+\.tm
usr/share/lua/[^/]+/posix/init\.lua
openssl/openssl-[^/]+/test/recipes/
usr/share/doc/libssl-doc/demos/
boringssl/src/third_party/[^/]+test[^/]+/[^/]+_test\.json
Additional Self-Hosted considerations
For GitGuardian Self-Hosted instances, scan frequency can be configured in the Admin Area:
- Time interval unit: seconds
- Default value: 86400 (1 day)
- Minimum value: 1800 (30 minutes)
Privacy and compliance
Data handling
GitGuardian processes your data solely to detect exposed secrets:
- Read-only access: We never require write access unless scoped to creating webhooks to receive and process real-time events
- Minimal data retention: We store only data and metadata necessary for incident management
- Encryption: All data in transit and at rest is encrypted
- Compliance: We follow the same data protection standards as our other integrations
Regional considerations
GitGuardian hosts its services in two AWS regions: eu-central-1 (Frankfurt) and us-west-2 (Oregon). Ensure your GitGuardian deployment region aligns with your data residency requirements. Contact support if you need guidance on compliance with local regulations.
User notification
Country-specific laws and regulations may require you to inform your users that your repositories are being scanned for secrets. Here is a suggestion for a message you may want to use:
As part of our internal information security process, the company scans its repositories for potential secrets leaks using GitGuardian. All data collected will be processed for the purpose of detecting potential leaks. To find out more about how we manage your personal data and to exercise your rights, please refer to our employee/partner privacy notice.
Please note that only repositories relating to the company's activity and business may be monitored and that users shall refrain from sharing personal or sensitive data not relevant to the repository's purpose.

